
WiFi and identity provider guides
Connect WiFi to the directory you already run, so joining and leaving the network follow joining and leaving the company.
In short
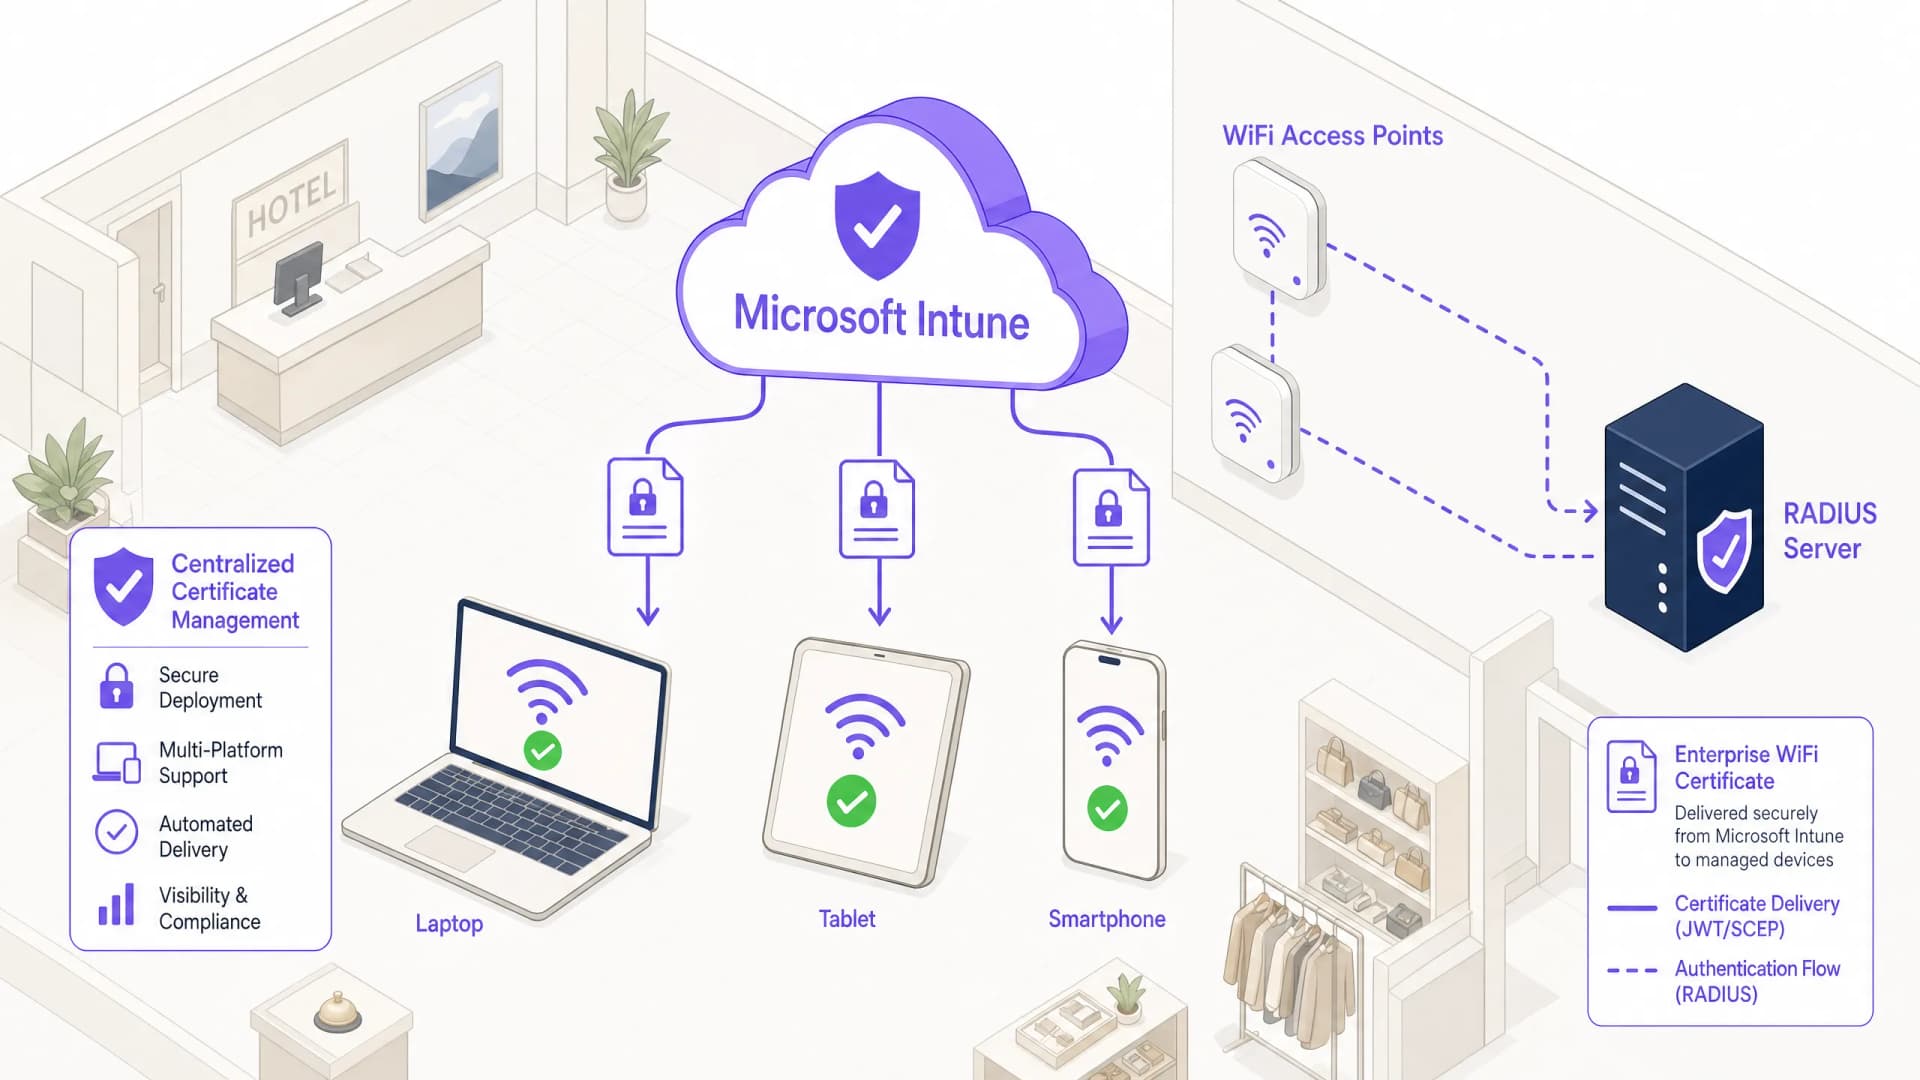
Linking WiFi to your identity provider means the network trusts the same accounts as email and single sign-on. Microsoft Entra ID, Okta or Google Workspace holds the user, Intune or another MDM pushes a certificate to the device, and cloud RADIUS checks both at connection time. Disable the account and WiFi access stops.
All 12 guides


Frequently asked questions
Can WiFi authenticate against Entra ID without on-premises Active Directory?
Yes. Entra ID does not offer a RADIUS endpoint for WiFi itself, so a cloud RADIUS service syncs users from it and checks their certificates. No domain controller or NPS server is needed.
How does Intune get WiFi certificates onto devices?
Through a SCEP or PKCS certificate profile and a WiFi profile assigned to the same group. The Intune guides below walk through both.
Does this work with Okta and Google Workspace?
Yes. Purple syncs users from Microsoft Entra ID, Okta and Google Workspace, so whichever directory you run stays the source of truth.
What happens to WiFi access when someone leaves?
Their account is disabled in the identity provider, the sync picks that up, and their certificate stops working at the next connection. Nobody has to change a shared password.