
RADIUS guides
How RADIUS decides who joins the network, and how to run it without a server of your own.
In short
RADIUS is the protocol access points use to ask a server whether a user or device may join the network. The server checks the credentials, returns accept or reject, and can assign a VLAN. Cloud RADIUS runs that server as a hosted service, so there is no on-premises NPS or FreeRADIUS box to patch.
All 21 guides
Cisco Meraki captive portal troubleshooting: splash page, walled garden and RADIUS checklist
Use this checklist to identify which of four faults is breaking your Cisco Meraki captive portal: splash page type, walled garden, grant URL hand-off or RADIUS reachability. You will be able to read the Meraki event log, match the symptom to its cause and apply the right fix without repeating SSID setup.
9 min read
Configuring RADIUS Authentication for Guest and Staff WiFi Networks
This technical reference guide outlines the architecture, configuration, and deployment of RADIUS authentication for enterprise guest and staff WiFi networks. It provides network architects and IT managers with the exact protocols, security standards, and troubleshooting methodologies required to build secure, scalable wireless access control systems.
8 min read
The Security Benefits of RADIUS as a Service for Hybrid Workforces
This technical reference guide explains how RADIUS as a Service secures network access for hybrid workforces across distributed venues. It covers the architecture, security benefits, and deployment steps for replacing on-premise RADIUS infrastructure with a cloud-managed authentication service. For IT managers and network architects at hotels, retail chains, stadiums, and public-sector organisations, this guide provides the evidence needed to evaluate and act on a cloud RADIUS migration this quarter.
9 min read
Integrating RADIUS as a Service with Cloud Directories (Azure AD & Google Workspace)
This technical reference guide details how to integrate RADIUS as a Service with cloud directories - Microsoft Entra ID and Google Workspace - for enterprise WiFi authentication. It covers the architectural shift from on-premises NPS to cloud-native RADIUS, the deployment of certificate-based EAP-TLS authentication, and the operational best practices for securing wireless access across hospitality, retail, and public-sector environments. For IT managers and network architects already invested in cloud identity, this guide bridges the gap between directory management and physical network security.
10 min read
Troubleshooting 802.1X Authentication Failures (RADIUS/EAP)
Step-by-step diagnostic guide for resolving 802.1X, EAP-TLS, PEAP, and RADIUS authentication errors on enterprise WiFi networks.
13 min read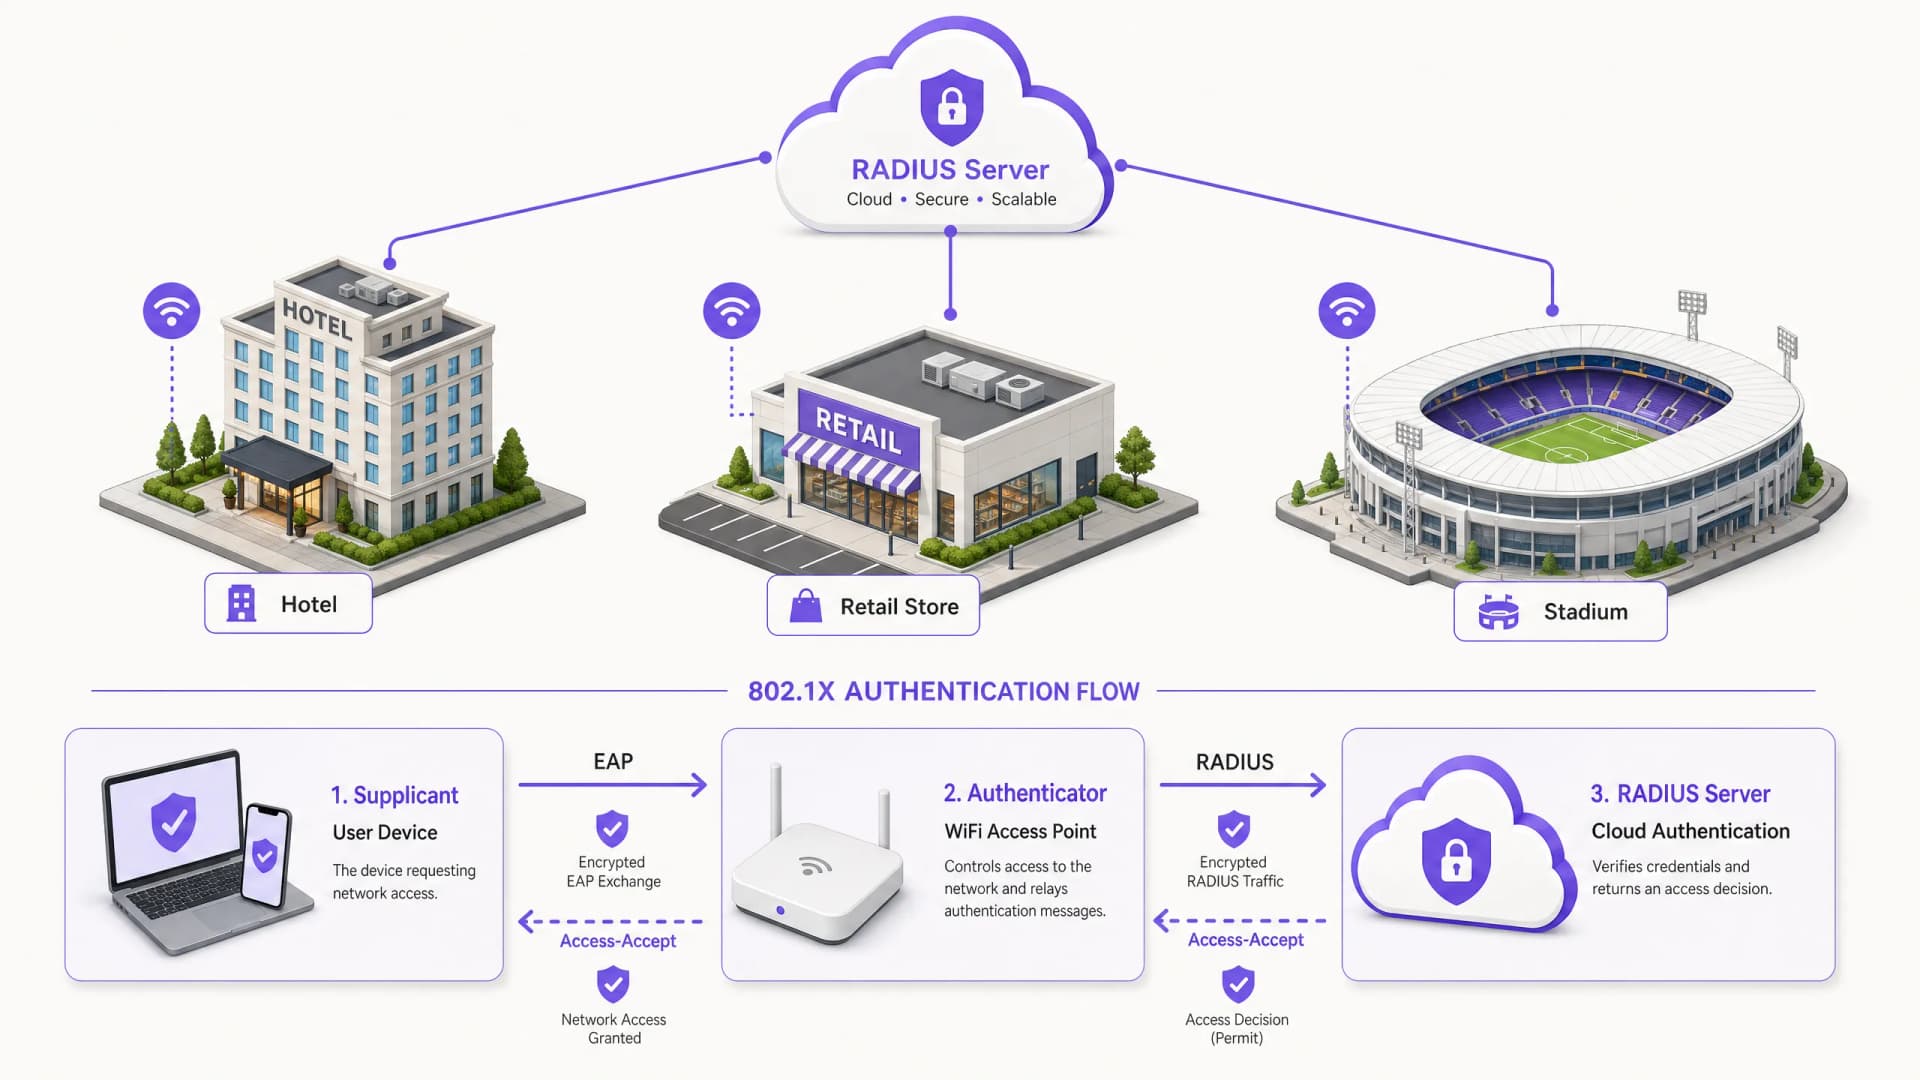
How to Implement 802.1X Authentication with Cloud RADIUS
This technical reference guide provides a comprehensive framework for implementing 802.1X authentication with Cloud RADIUS across distributed enterprise estates. It details the architecture, EAP method selection, deployment sequencing, and risk mitigation strategies required to secure network access while eliminating the operational overhead of on-premises infrastructure.
5 min read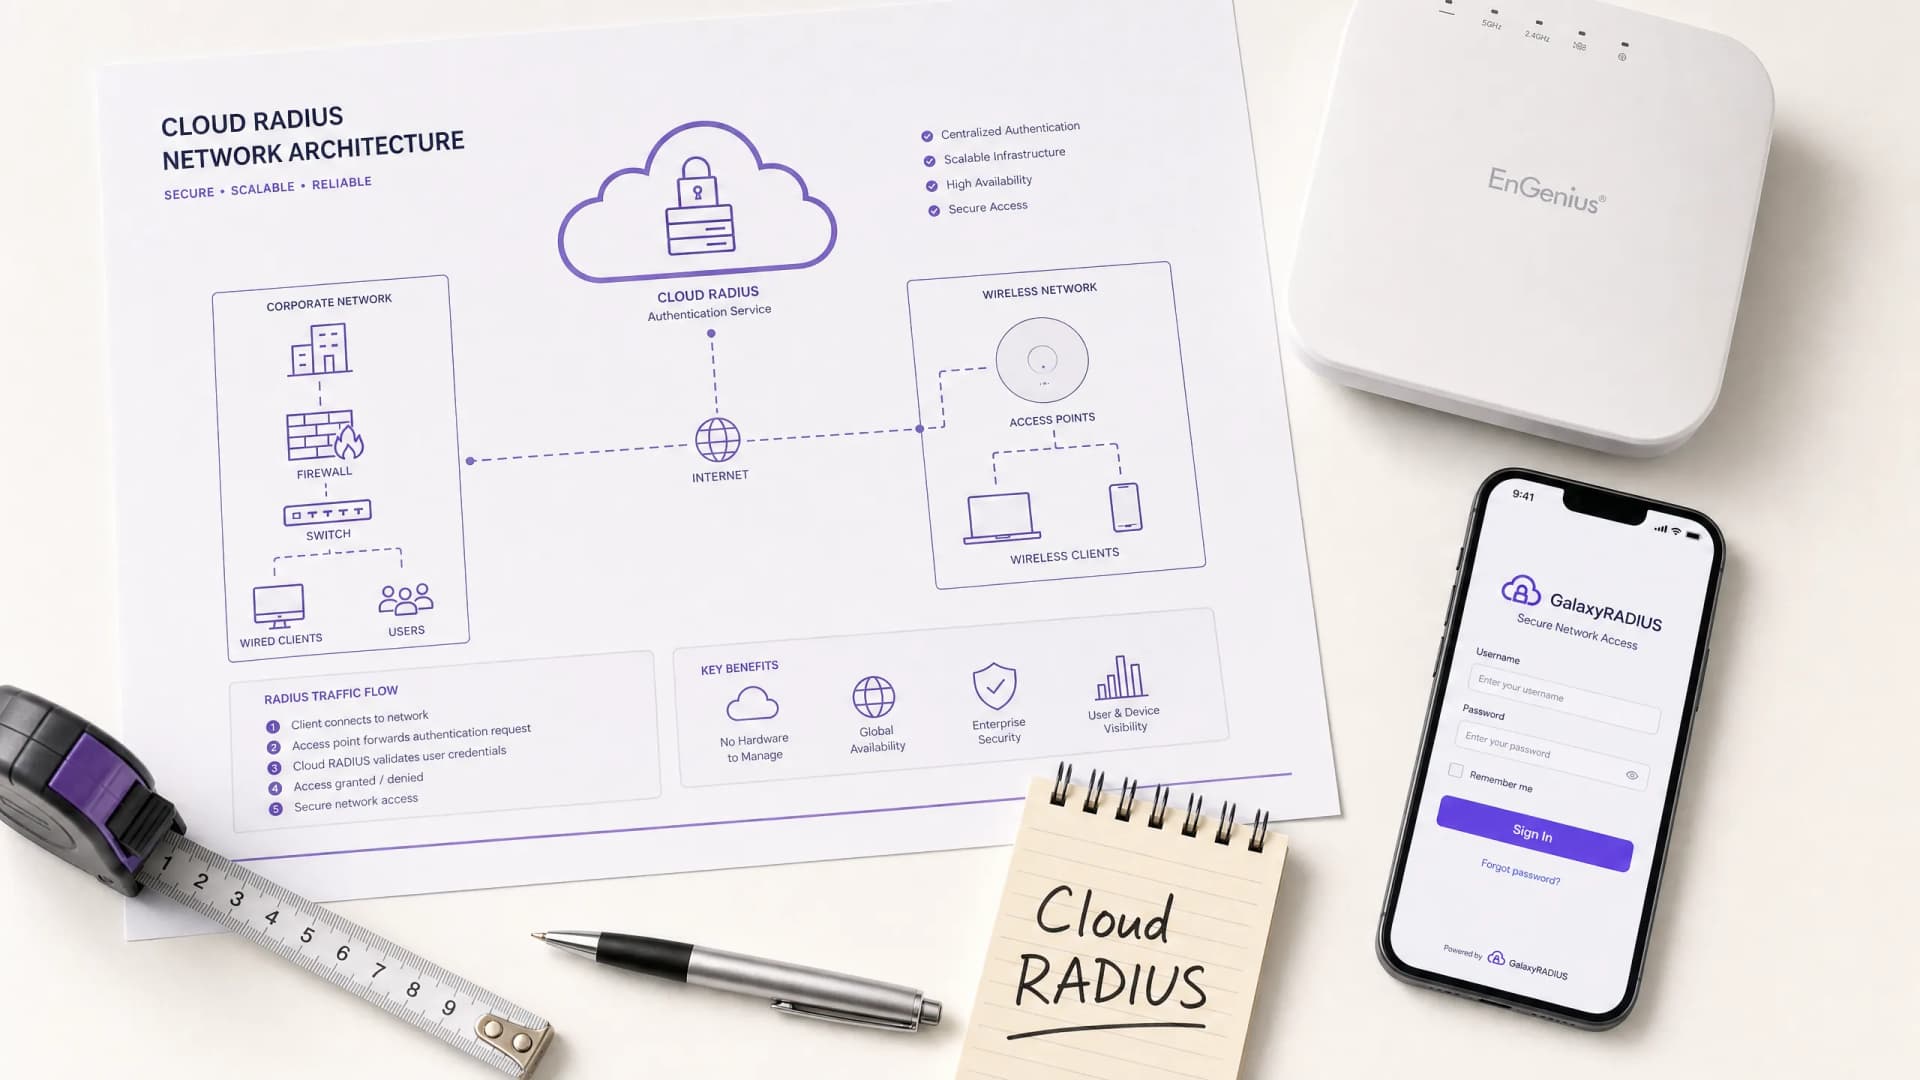
What is Cloud RADIUS? A Comprehensive Guide to RADIUS as a Service
This comprehensive guide explores Cloud RADIUS (RADIUS as a Service), detailing its architecture, EAP methods, and implementation strategies. It provides IT leaders with actionable insights on migrating from on-premises servers to a scalable, secure, and compliant cloud-based authentication model.
5 min read
Migrating from On-Premises RADIUS (NPS) to RADIUS as a Service
This authoritative guide details the technical architecture, implementation methodology, and business impact of migrating from on-premises Microsoft Network Policy Server (NPS) to a cloud-native RADIUS as a Service model. It provides IT leaders and network architects with practical frameworks to reduce operational overhead, eliminate single points of failure, and secure enterprise authentication across distributed venues.
5 min read
Configuring RADIUS Policies for Fine-Grained Network Access Control
This authoritative guide provides IT managers, network architects, and venue operations directors with a complete technical blueprint for configuring RADIUS policies to achieve fine-grained network access control. It covers 802.1X architecture, dynamic VLAN assignment, EAP method selection, and phased deployment strategies. Real-world implementation scenarios from hospitality and retail demonstrate how these techniques deliver measurable compliance, security, and operational ROI.
6 min read
RadSec: How RADIUS over TLS Improves WiFi Authentication Security
This authoritative technical reference explains how RadSec (RFC 6614) secures enterprise WiFi authentication by wrapping traditional RADIUS traffic in TLS encryption. Designed for IT managers and network architects, it covers architecture, deployment strategies, and practical steps to mitigate the risks of unencrypted UDP RADIUS traffic across corporate and guest networks.
4 min read
How to set up a RADIUS server for WiFi authentication: Step-by-step 802.1X guide
Configure FreeRADIUS, Windows Server NPS, and Cloud RADIUS for enterprise 802.1X WiFi authentication. Step-by-step guide covering shared secrets, EAP-TLS certificates, dynamic VLAN assignment, and Microsoft Entra ID integration.
8 min read
Mitigating RADIUS Vulnerabilities: A Security Hardening Guide
This guide provides a comprehensive, actionable reference for IT managers, network architects, and CTOs responsible for enterprise WiFi infrastructure across hospitality, retail, events, and public-sector environments. It covers the full attack surface of RADIUS server deployments - from MD5 collision vulnerabilities and weak shared secrets to unencrypted UDP transport and misconfigured EAP methods - and delivers a prioritised hardening roadmap aligned with IEEE 802.1X, PCI DSS, and GDPR requirements. Organisations that implement these recommendations will materially reduce their exposure to credential-based network attacks, meet compliance obligations, and build a defensible security posture for their guest and corporate WiFi infrastructure.
12 min read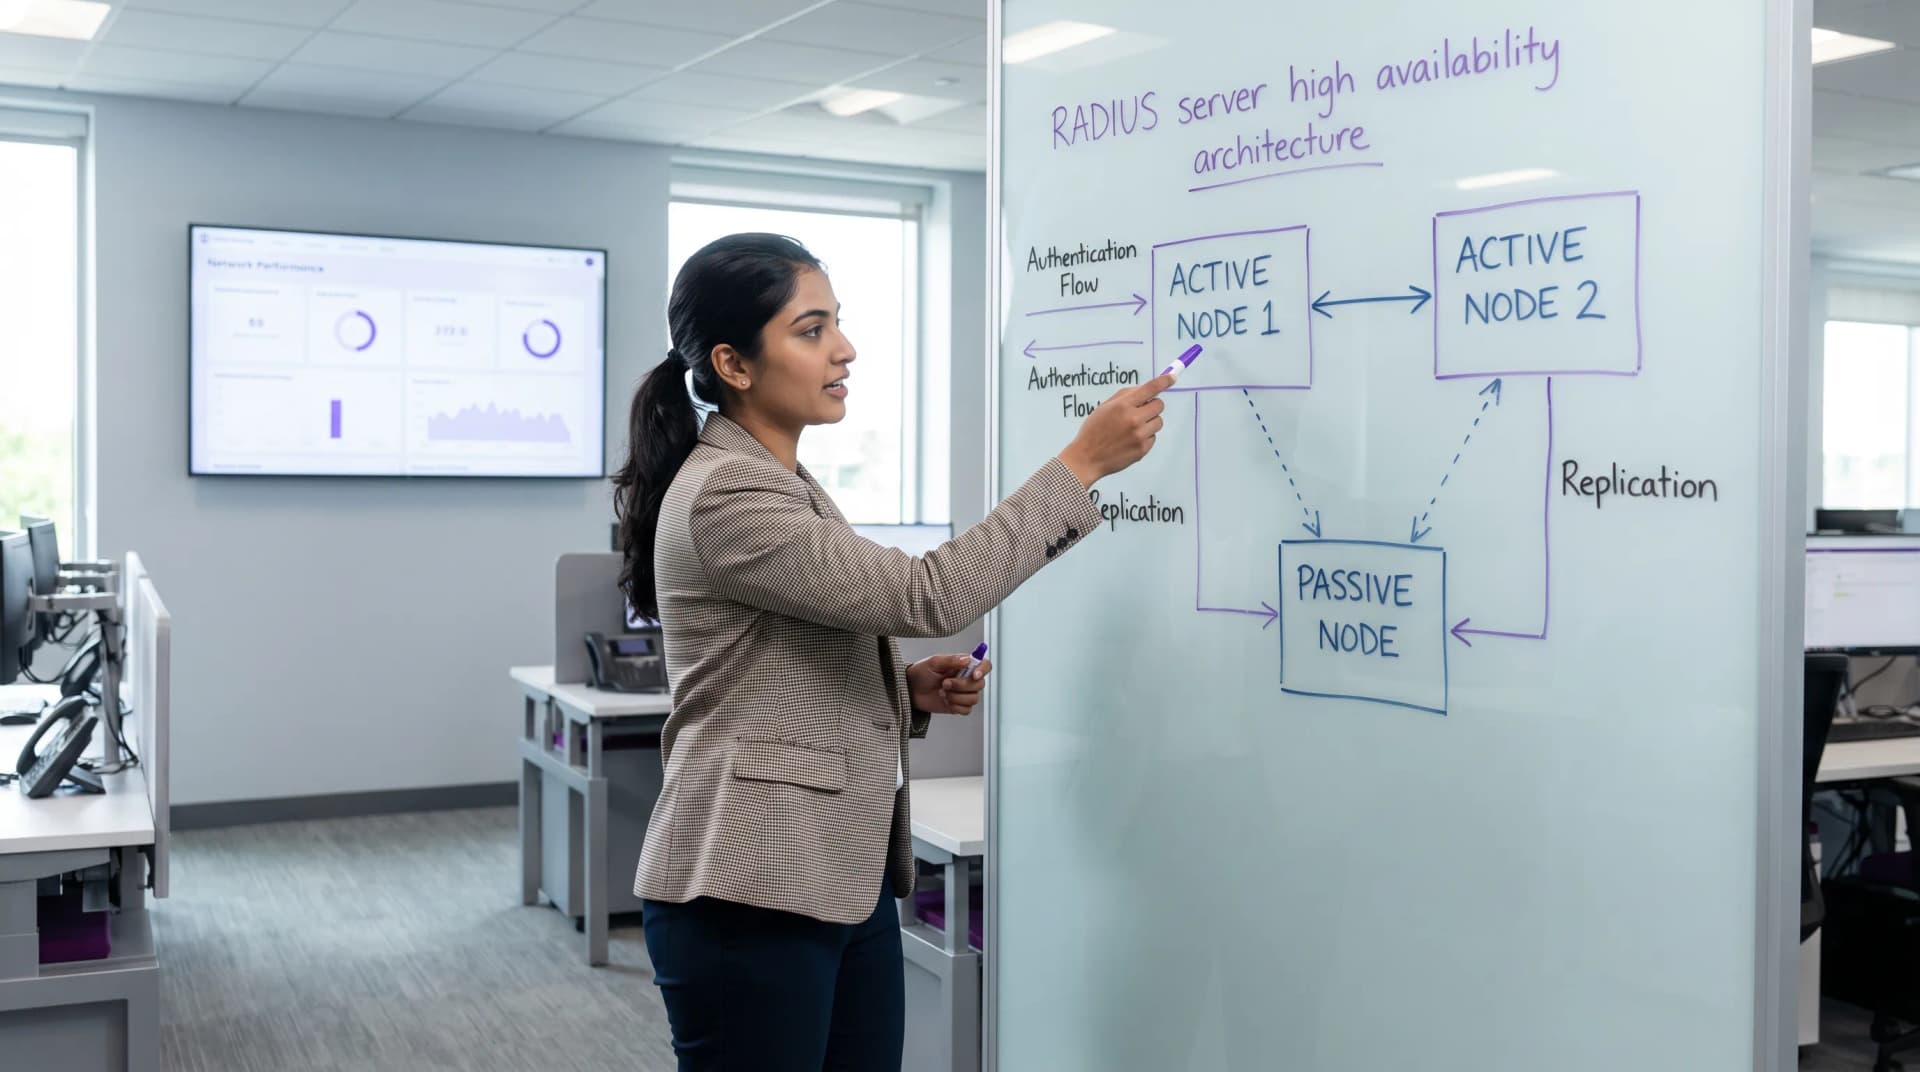
RADIUS Server High Availability: Active-Active vs Active-Passive
A definitive technical reference guide for IT managers and network architects evaluating RADIUS high availability architectures. It contrasts Active-Active and Active-Passive deployments, details database replication requirements, and explains how Cloud RADIUS mitigates failover latency for enterprise venues.
6 min read
Cloud RADIUS vs on-premise RADIUS: decision guide for IT teams
Compare Cloud RADIUS and on-premise RADIUS (FreeRADIUS, NPS) for enterprise 802.1X WiFi security. Architectural comparison, TCO analysis, SCEP EAP-TLS integration, and WAN resilience.
10 min read
Okta and RADIUS: Extending Your Identity Provider to WiFi Authentication
This guide provides a comprehensive technical reference for IT administrators at Okta-centric organisations who want to extend their cloud identity provider to WiFi authentication using the Okta RADIUS agent. It covers the full authentication architecture, MFA enforcement trade-offs, dynamic VLAN assignment via RADIUS attribute mapping, and the critical decision between password-based EAP-TTLS and certificate-based EAP-TLS. Venue operators and enterprise IT teams will find actionable deployment guidance, real-world case studies from hospitality and retail, and a clear framework for integrating Okta RADIUS alongside dedicated guest WiFi solutions.
11 min read
Jamf and RADIUS: Certificate-Based WiFi Authentication for Apple Device Fleets
This technical reference guide provides IT managers, network architects, and CTOs with actionable steps to deploy certificate-based 802.1X WiFi authentication for Apple device fleets using Jamf Pro and RADIUS. It covers the full SCEP certificate provisioning workflow, WiFi configuration profile structure, RADIUS integration requirements, and real-world implementation scenarios from healthcare and enterprise environments. The guide is essential for any organisation seeking to eliminate password-based WiFi vulnerabilities, reduce helpdesk overhead, and achieve compliance with PCI DSS and GDPR network access standards.
9 min read
RADIUS Accounting: Tracking Sessions, Usage, and Audit Logs
This guide provides a comprehensive technical reference on RADIUS accounting - how it records WiFi session start, stop, and interim-update data, what attributes are captured, and how to leverage that data for security auditing, GDPR compliance, and capacity planning. It is essential reading for network operations and security teams who need defensible audit trails from WiFi authentication events, and for venue operators seeking to integrate session data into SIEM platforms and analytics dashboards.
9 min read
Dynamic VLAN Assignment with RADIUS: Segmenting Users by Role
This guide provides a comprehensive technical overview of implementing dynamic VLAN assignment using RADIUS attributes. It details how enterprise venues can automate network segmentation for staff, guests, and IoT devices to enhance security and reduce manual configuration overhead.
5 min read
Hardening RADIUS against MD5 collision attacks (BlastRADIUS)
Mitigate CVE-2024-3596 BlastRADIUS attacks. Enforce RADIUS Message-Authenticator, patch FreeRADIUS & Cisco ISE, and migrate to 802.1X EAP-TLS.
8 min read
Staff WiFi security guide: 802.1X, WPA3 & RADIUS access
Technical reference for IT leaders on designing secure staff WiFi networks with 802.1X authentication, WPA3-Enterprise, cloud RADIUS, and network segmentation.
7 min read
What is RADIUS Authentication and How Does It Work?
This guide provides a definitive technical reference on RADIUS authentication for IT leaders managing enterprise and guest WiFi deployments. It demystifies the AAA protocol, explains how 802.1X and EAP methods work together, and details how Purple's cloud-based platform simplifies deployment for hotels, retail chains, stadiums, and public-sector organisations. Readers will leave with a clear implementation roadmap, real-world case studies, and the decision frameworks needed to migrate from insecure pre-shared keys to a robust, identity-driven network access control architecture.
6 min read
Frequently asked questions
What does RADIUS do on a WiFi network?
It authenticates. When a device connects to a WPA2- or WPA3-Enterprise network, the access point forwards the request to a RADIUS server, which accepts or rejects it and can return a VLAN for that user.
What is cloud RADIUS?
Cloud RADIUS is a hosted RADIUS service. Purple RADIUS-as-a-Service covers WPA2/3-Enterprise, EAP-TLS, PEAP and iPSK, with multi-region failover and user sync from Entra ID, Okta and Google Workspace.
Do I still need Windows NPS?
Not with cloud RADIUS. The access points send requests to the hosted service instead of a server in your building, so there is no NPS or FreeRADIUS host to maintain.
Which ports does RADIUS use?
UDP 1812 for authentication and UDP 1813 for accounting. RadSec carries RADIUS inside TLS over TCP 2083, which is the safer way to send it across the internet.
Got a question about your own network?
Our team works with IT teams and venue operators across 80,000 venues. Book a 20-minute call and we will show you how others solved it.