
Technical WiFi guides
Deep, expert-led technical guides on guest WiFi, analytics, captive portals, and venue technology.
Ready to move from research to rollout? See how Purple's captive portal software handles branded guest sign-in, analytics, and compliance in one platform.
54 guides in Security

Is Hospital WiFi Safe? What Patients and Visitors Should Know
This comprehensive technical reference guide examines the security architecture of hospital guest WiFi networks. It provides IT managers and venue operators with actionable implementation strategies, focusing on network segmentation, encryption standards, and compliance frameworks to ensure patient data remains protected without compromising clinical operations.

Is Airport WiFi Safe? A Traveller's Security Guide
This guide provides an authoritative technical reference for IT managers, network architects, and venue operations directors on the security risks of airport WiFi and how to mitigate them. It covers the full threat landscape — from Evil Twin access points to rogue DHCP servers — and delivers a practical, standards-based deployment framework using IEEE 802.1X, WPA3, and network segmentation. It also maps Purple's Guest WiFi and analytics platform to each risk vector, providing concrete integration points for operators looking to deploy secure, GDPR-compliant, and commercially viable public WiFi.

Is Hotel WiFi Safe? What Every Traveller Needs to Know
This comprehensive technical guide details the specific security risks inherent in hotel WiFi networks, including rogue APs and MITM attacks. It provides actionable, vendor-neutral implementation steps for IT managers and network architects to secure their wireless infrastructure and leverage managed guest WiFi platforms.

Is Public WiFi Safe? The Definitive Guide
This definitive guide provides enterprise IT leaders with actionable strategies for architecting secure public WiFi networks. It details the technical mitigation of primary threats like MITM attacks and rogue access points, while outlining how to leverage platforms like Purple to ensure compliance, protect corporate infrastructure, and safely monetise guest connectivity.

How to Monitor WiFi Network Traffic: A Guide for IT Teams
This technical guide provides actionable strategies for monitoring enterprise WiFi traffic, focusing on architecture, security, and performance. It equips IT teams in hospitality, retail, and public sectors with the frameworks needed to deploy scalable, secure network monitoring solutions.

BYOD WiFi Security: How to Safely Let Personal Devices on Your Network
A pragmatic, vendor-neutral guide for IT leaders on securing BYOD WiFi access. It covers the implementation of 802.1X authentication, MDM integration, and strict network segmentation to protect corporate assets while enabling personal devices.

The Most Secure Method of WiFi Authentication: A Comparison
This technical reference guide provides a definitive ranked comparison of WiFi authentication methods - from the deprecated WEP standard through to EAP-TLS certificate-based authentication - helping IT managers, network architects, and CTOs at enterprise venues make informed, compliance-aligned security decisions. It covers the technical architecture of each protocol, real-world deployment scenarios in hospitality and retail, and practical implementation guidance for organizations operating under PCI DSS and CCPA/CPRA obligations. For venue operators and IT teams, this guide translates complex cryptographic standards into actionable deployment decisions with measurable business outcomes.

WPA-PSK Explained: What It Is, How It Works, and Its Security Risks
This authoritative technical reference breaks down the mechanics of WPA-PSK - its 4-way handshake, cryptographic architecture, and inherent security vulnerabilities - and explains precisely why enterprise networks must transition to robust 802.1X or managed captive portal architectures. It provides actionable deployment guidance for IT leaders managing complex venue environments across hospitality, retail, events, and public-sector organizations.

What Is WiFi Security? A Complete Guide to Wireless Network Security
A comprehensive technical reference for IT leaders on securing enterprise wireless networks. This guide covers the evolution of encryption protocols, architectural best practices for segmentation, and defense strategies against common WiFi threats.

PCI DSS Compliance for Retail WiFi Networks
This technical reference guide details the PCI DSS v4.0 requirements that apply specifically to retail WiFi networks, covering network segmentation architecture, encryption standards, authentication controls, and audit trail requirements. It provides actionable implementation guidance for IT managers and network architects who need to secure payment data while safely supporting separate guest and corporate wireless access.

HIPAA-compliant guest WiFi for healthcare providers
A practical compliance guide for healthcare IT teams deploying HIPAA guest WiFi. Learn about network segmentation, data handling, and BAA requirements.

CCPA vs GDPR: Global Privacy Compliance for Guest WiFi Data
This guide provides a comprehensive technical comparison of CCPA and GDPR requirements for guest WiFi deployments. It delivers actionable strategies for IT leaders and network architects to build a unified, dual-compliant consent framework that mitigates regulatory risk while preserving the commercial value of first-party data.
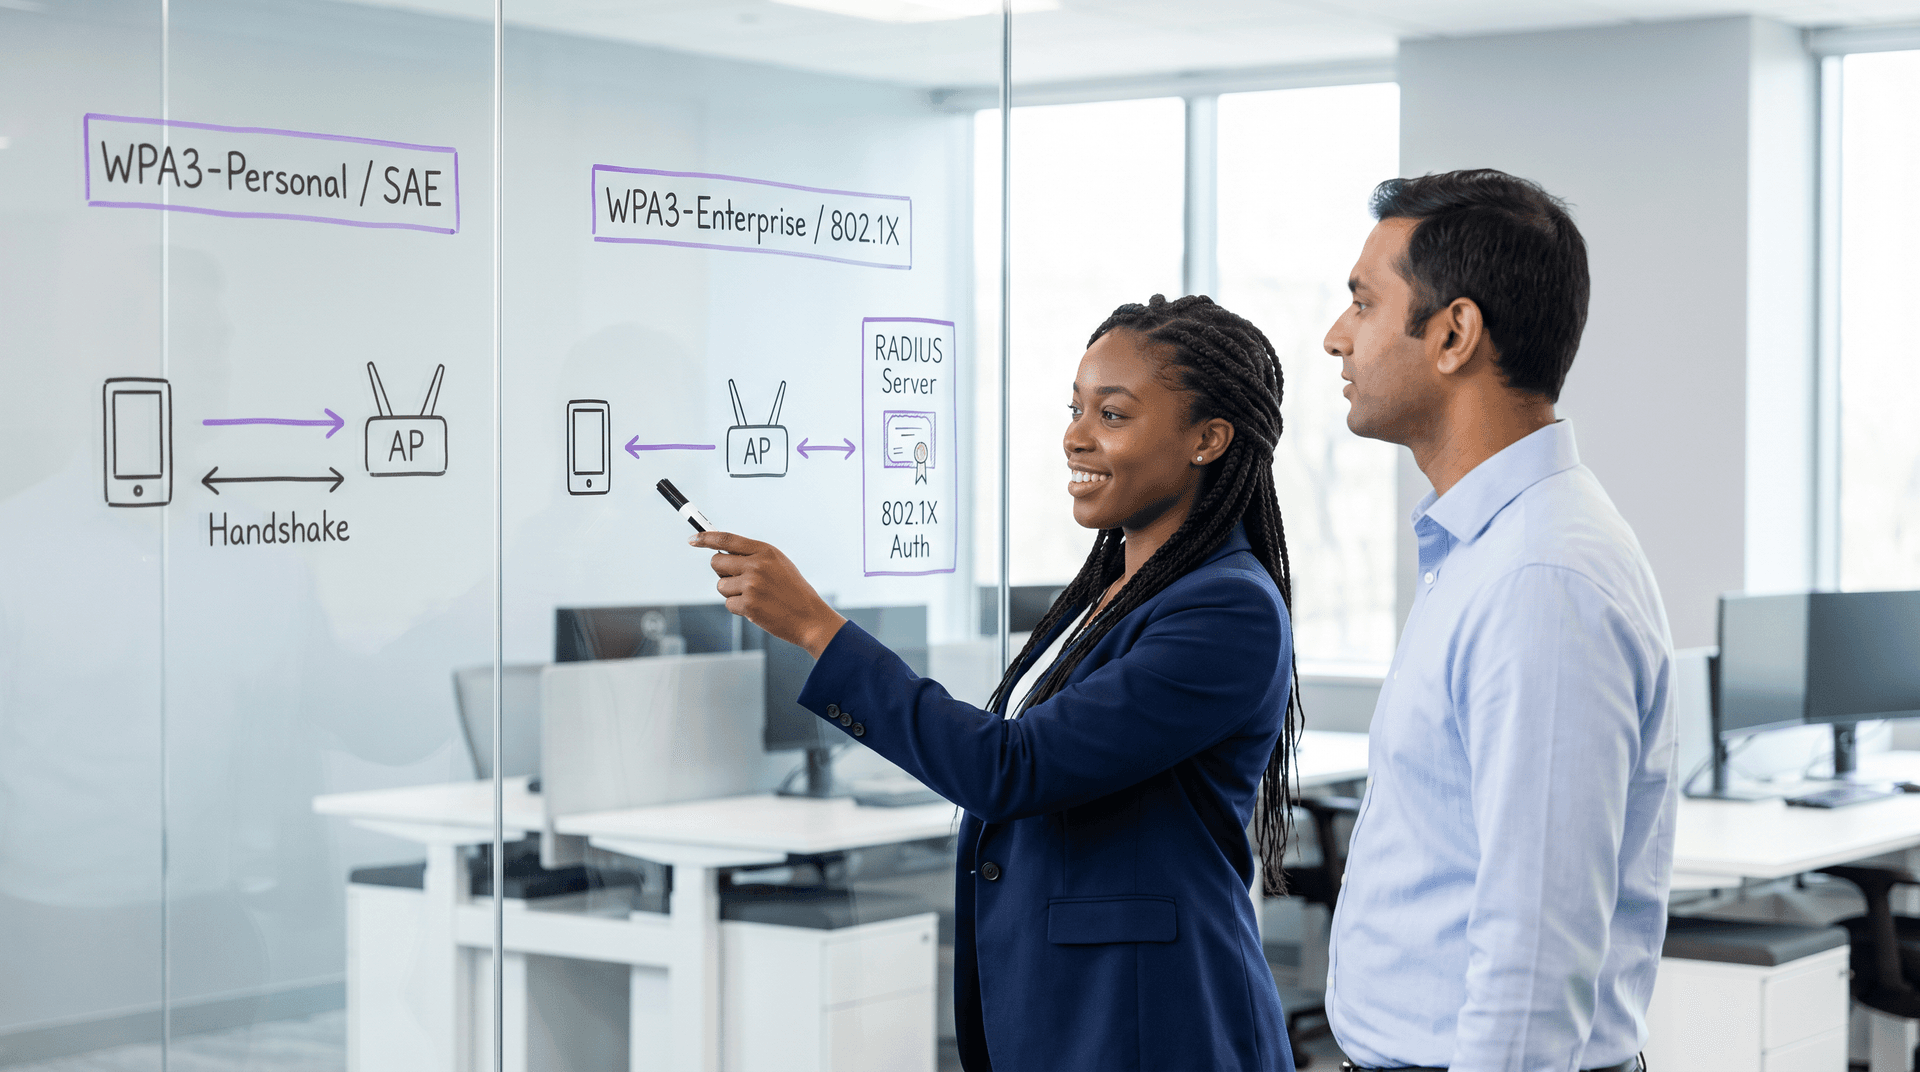
WPA3 Personal vs Enterprise: WiFi Security Comparison
Technical comparison of WPA3 Personal (SAE) vs WPA3 Enterprise (802.1X). Learn encryption differences, RADIUS authentication, and enterprise deployment steps.
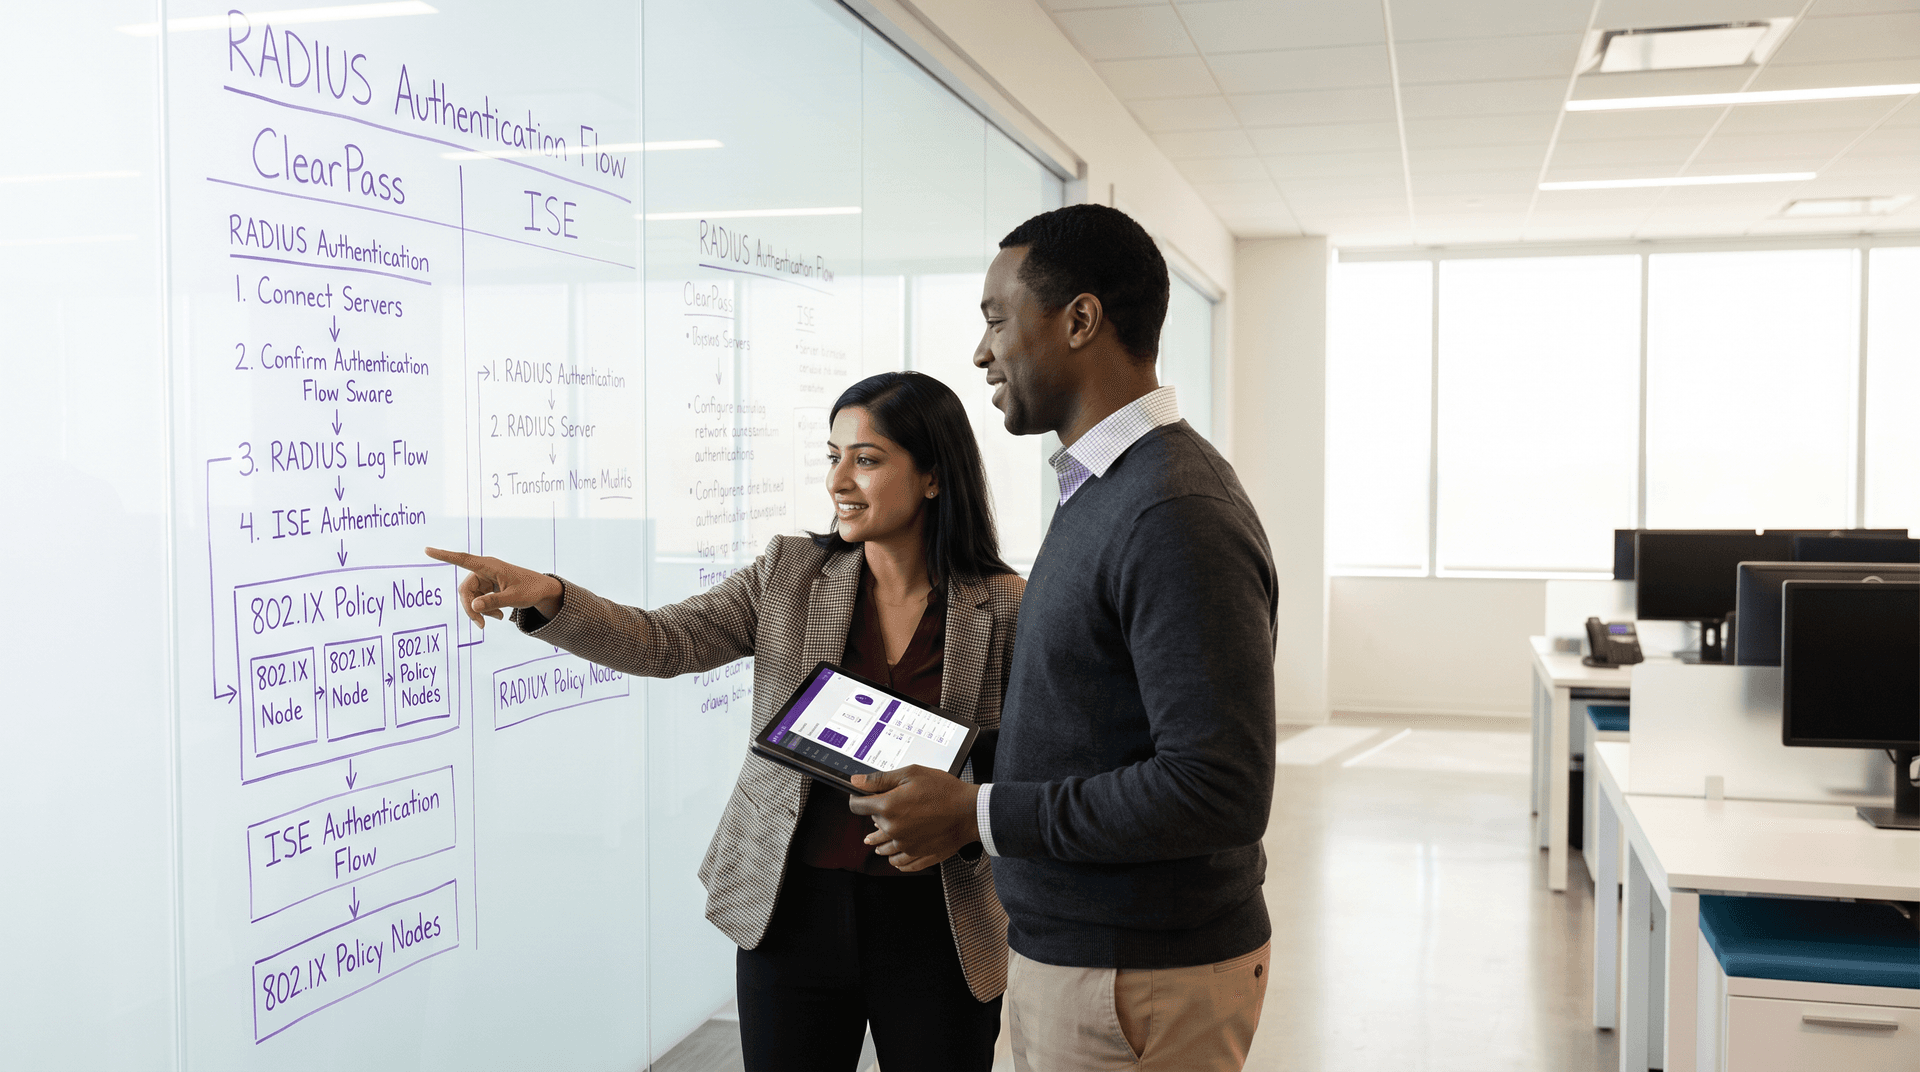
Aruba ClearPass vs Cisco ISE: enterprise NAC platform comparison
Compare Aruba ClearPass Policy Manager and Cisco ISE. Evaluate multi-vendor RADIUS AAA, 802.1X policy engines, licensing costs, and guest WiFi integration.
Rogue AP Detection: Protecting Venue WiFi from Impersonation Attacks
This guide provides a comprehensive technical reference for IT managers, network architects, and venue operations directors on deploying Wireless Intrusion Prevention Systems (WIPS) to detect and neutralise rogue access points and evil twin attacks. It covers detection methodologies, legal countermeasures, compliance requirements, and real-world implementation scenarios across hospitality, retail, and public-sector environments. Organisations that implement the strategies outlined here will strengthen their wireless security posture, reduce compliance risk, and protect both their infrastructure and their users from WiFi impersonation threats.

ISO 27001 Guest WiFi: A Compliance Primer
This authoritative technical reference maps guest WiFi deployments directly to ISO 27001:2022 controls, detailing network segregation, logging, and risk treatment requirements. It provides actionable guidance for IT managers and network architects on generating audit-ready evidence and leveraging vendor SOC 2 attestations to satisfy ISMS supplier assurance mandates.

DNS Filtering for Guest WiFi: Blocking Malware and Inappropriate Content
This guide provides IT managers, network architects, and venue operations directors with a definitive technical reference for deploying DNS filtering on guest WiFi networks. It covers the architecture of DNS-level threat blocking, a vendor comparison of leading cloud DNS services, step-by-step implementation guidance, and real-world case studies from hospitality and retail environments. DNS filtering is the most cost-effective first line of defense against malware, phishing, and inappropriate content on public-facing networks, and this guide equips teams to deploy it confidently and in compliance with PCI DSS, CCPA/CPRA, and HIPAA requirements.

Guest WiFi Session Timeouts: Balancing UX and Security
This guide provides a practical framework for configuring guest WiFi session timeouts, balancing seamless user experience with robust security. It covers idle timeouts, absolute timeouts, re-authentication strategies, and industry-specific deployment scenarios for IT and venue operations leaders.

PEAP-MSCHAPv2: Why It Is Still Common, Why It Is Risky, and How to Move On
A comprehensive technical reference guide detailing the critical security vulnerabilities of PEAP-MSCHAPv2, including evil twin attacks and credential capture. It provides a practical, vendor-neutral roadmap for IT teams to migrate enterprise WiFi networks to secure, certificate-based EAP-TLS authentication.

Zero Trust WiFi Architecture: Applying Zero Trust to Venue Networks
A comprehensive technical reference guide detailing how venue operators can apply Zero Trust principles to enterprise WiFi networks. It covers continuous verification, micro-segmentation, and device posture enforcement to secure hospitality, retail, and public-sector environments against lateral movement and compliance risks.

PKI Fundamentals for WiFi Administrators: Certificates, CAs, and Trust Chains
This technical reference guide explains the foundational concepts of Public Key Infrastructure (PKI) for enterprise WiFi administrators, covering certificate authorities, trust chains, and X.509 certificates. It details how PKI underpins EAP-TLS mutual authentication and provides actionable deployment guidance for IT teams in hospitality, retail, and public-sector environments. Understanding PKI is a mandatory prerequisite for deploying certificate-based staff WiFi authentication with Purple.

The Ultimate Guide to OpenRoaming Architecture and Authentication
This guide provides an authoritative technical reference on WBA OpenRoaming architecture, covering the Passpoint foundation, RADIUS federation, RadSec mTLS security, and step-by-step deployment guidance for enterprise venues. It equips IT managers, network architects, and venue operators with the knowledge to replace captive portals with seamless, secure, and compliant WiFi connectivity that delivers measurable ROI.

OCSP and Certificate Revocation for WiFi Authentication
This comprehensive guide explores the critical mechanisms of certificate revocation in enterprise WiFi environments, focusing on the transition from CRLs to OCSP. It provides actionable implementation strategies for IT teams managing large-scale, high-density networks where real-time security and low latency are paramount.

Device Posture Assessment for Network Access Control
This technical guide explains how device posture assessment works for Network Access Control (NAC), detailing the architecture, MDM integration, and remediation flows required to implement Zero Trust WiFi in enterprise and venue environments.
Got questions about your specific setup?
Our team works with venue operators, IT managers, and network engineers across 80,000 venues. Book a 20-minute call and we will show you how others like you solved it.
