Technical WiFi guides

Deep, expert-led technical guides on guest WiFi, analytics, captive portals, and venue technology.

Ready to move from research to rollout? See how Purple's captive portal software handles branded guest sign-in, analytics, and compliance in one platform.

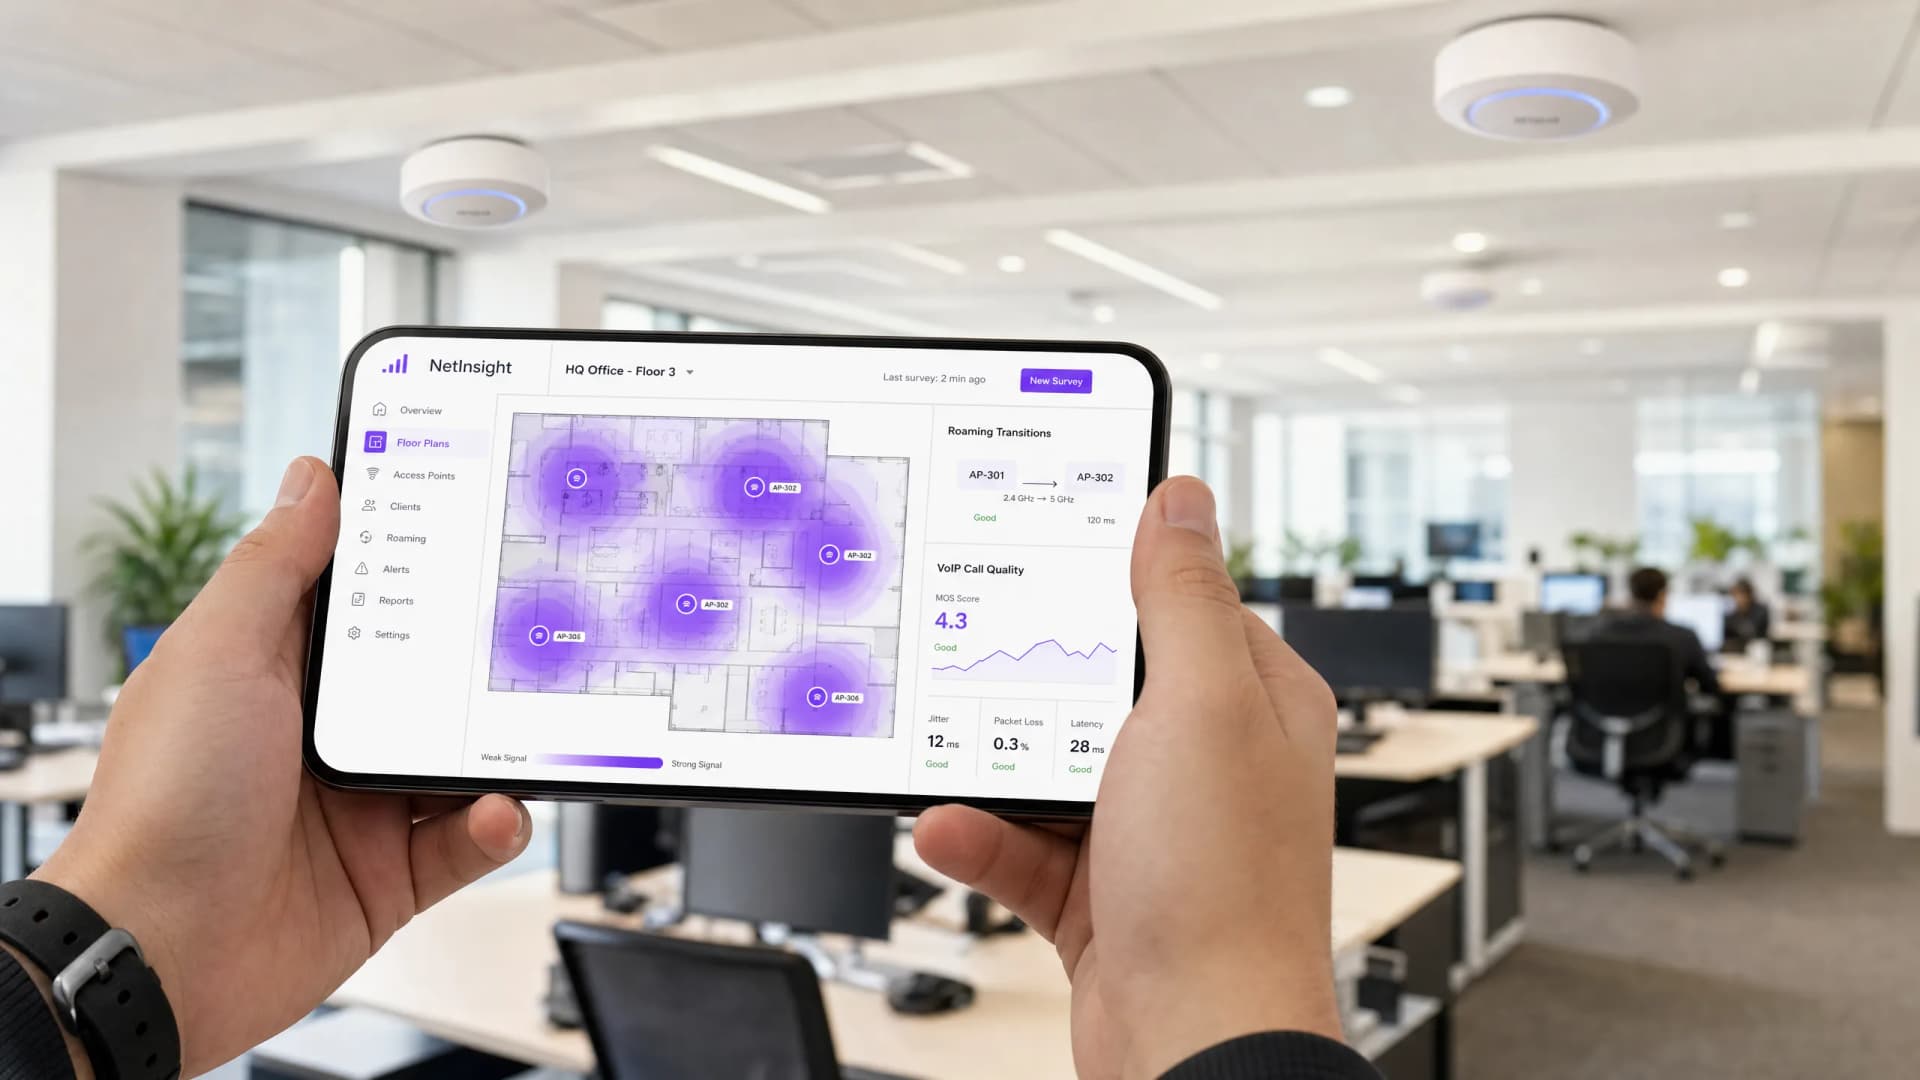
Roaming Optimisation for VoIP and Video Calls on Corporate WiFi
Staff WiFi

Roaming Optimisation for VoIP and Video Calls on Corporate WiFi

This guide provides IT managers, network architects, and CTOs with a comprehensive, vendor-neutral blueprint for optimising WiFi roaming to support seamless VoIP and video calls on corporate staff networks. It covers the IEEE 802.11k/r/v protocol stack, WMM QoS configuration, RF cell design, and end-to-end wired QoS mapping required to achieve sub-50ms handoff latency. Applicable across hospitality, retail, healthcare, and large-venue environments, this reference includes real-world implementation scenarios, troubleshooting frameworks, and a measurable ROI analysis.

10 mins read2k words
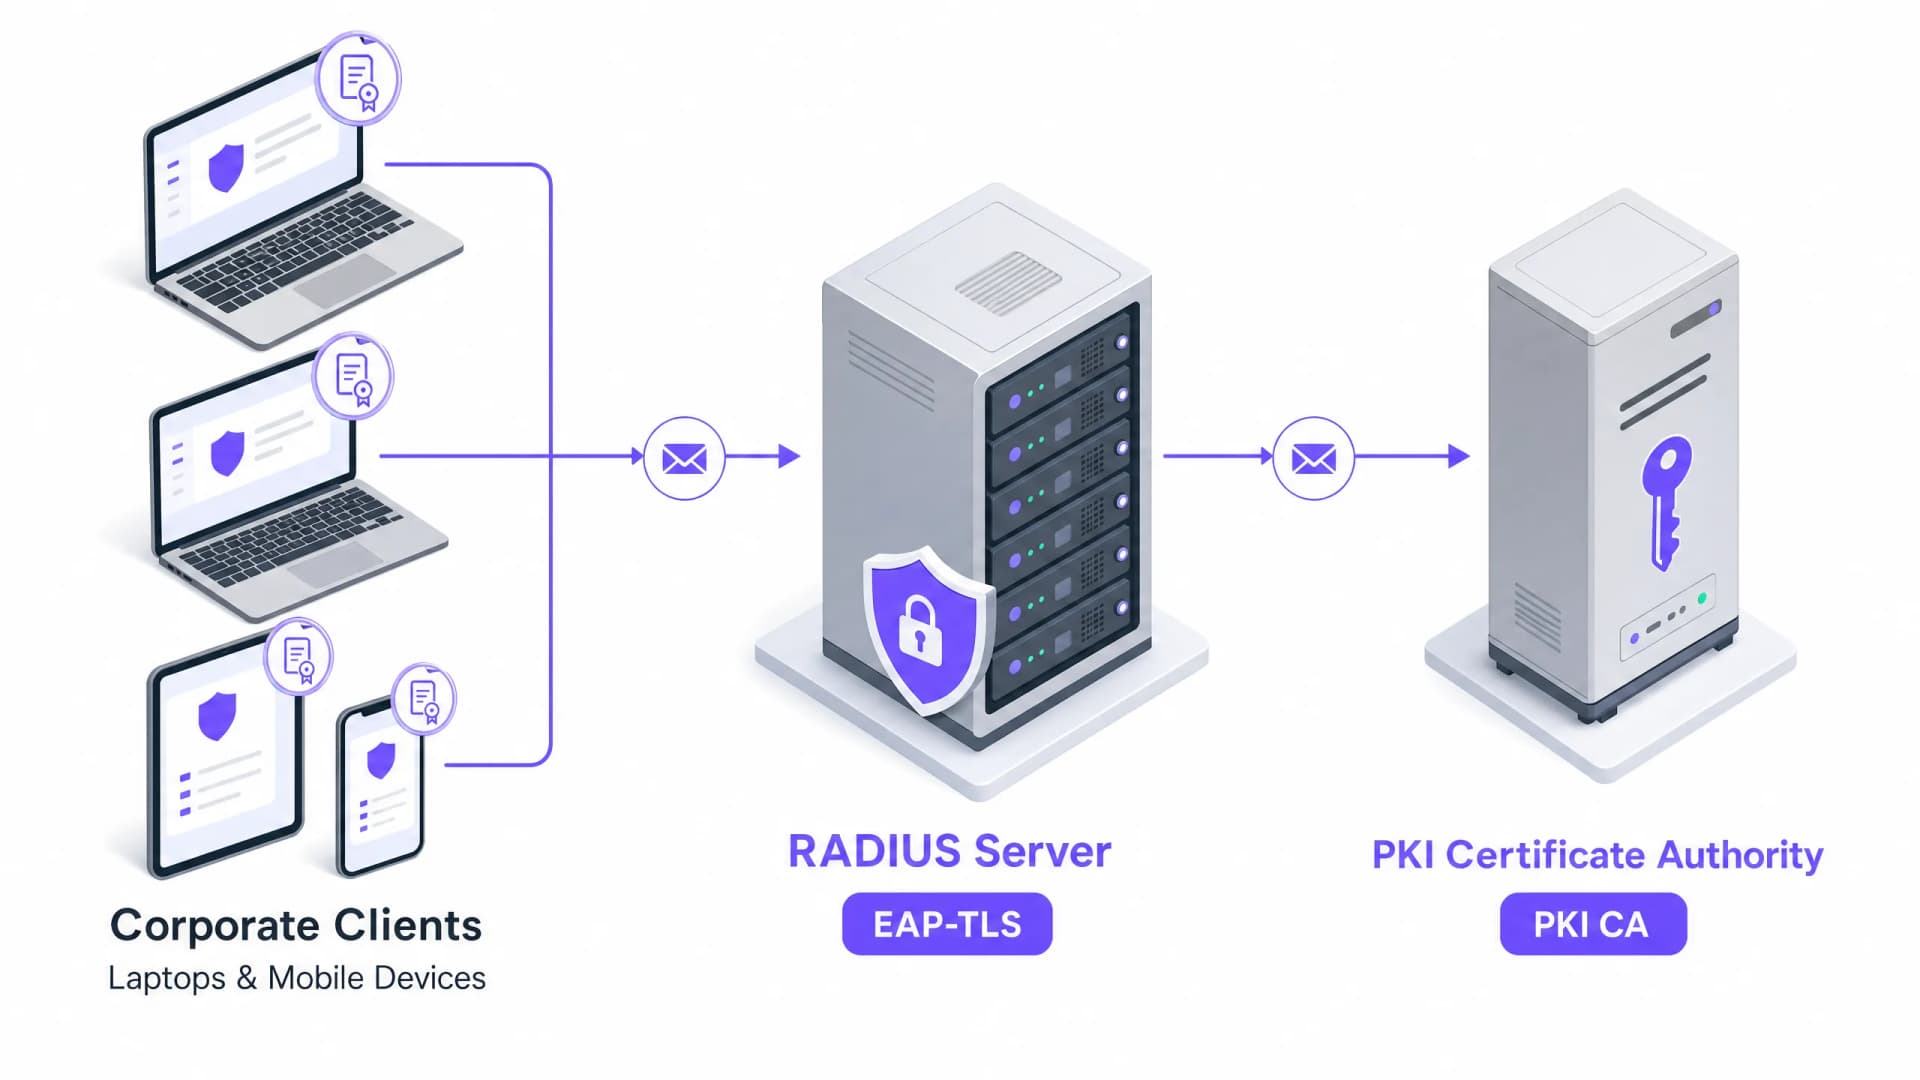
Certificate-Based Authentication for Corporate Devices (EAP-TLS)
Staff WiFi

Certificate-Based Authentication for Corporate Devices (EAP-TLS)

This authoritative technical reference guide covers the architecture, deployment, and operational best practices of EAP-TLS certificate-based authentication for corporate devices. Designed for IT architects and venue operations leaders, it provides a practical roadmap to eliminate password-based credential risks and achieve robust 802.1X network access control across multi-site enterprise environments.

13 mins read3k words
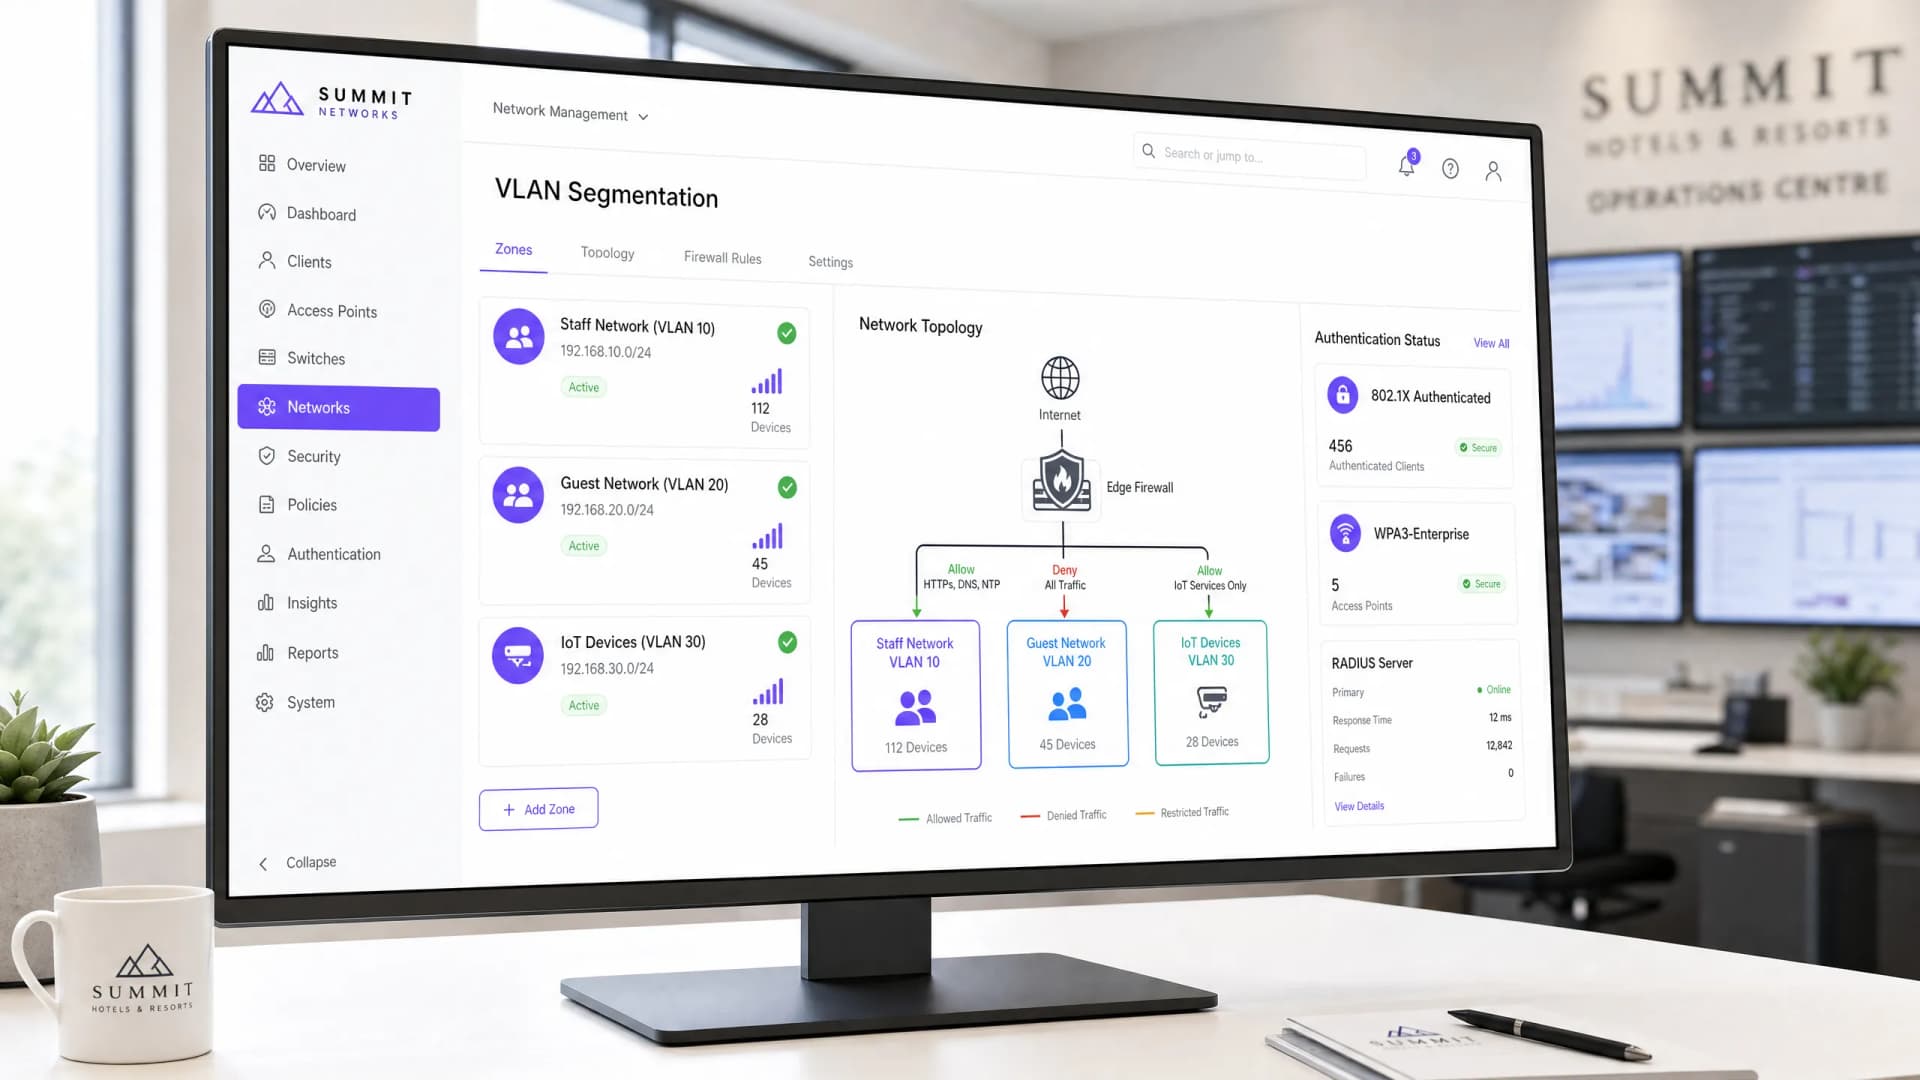
Designing Secure Staff WiFi Networks Separated from Guest Traffic
Staff WiFi

Designing Secure Staff WiFi Networks Separated from Guest Traffic

An authoritative technical reference guide for network architects and IT leaders on designing secure, high-performance staff WiFi networks. It details the logical and physical segmentation of operational traffic from public guest networks using VLANs, 802.1X authentication, and WPA3-Enterprise to satisfy compliance mandates (PCI DSS, GDPR) and eliminate lateral movement security risks.

3 mins read1k words
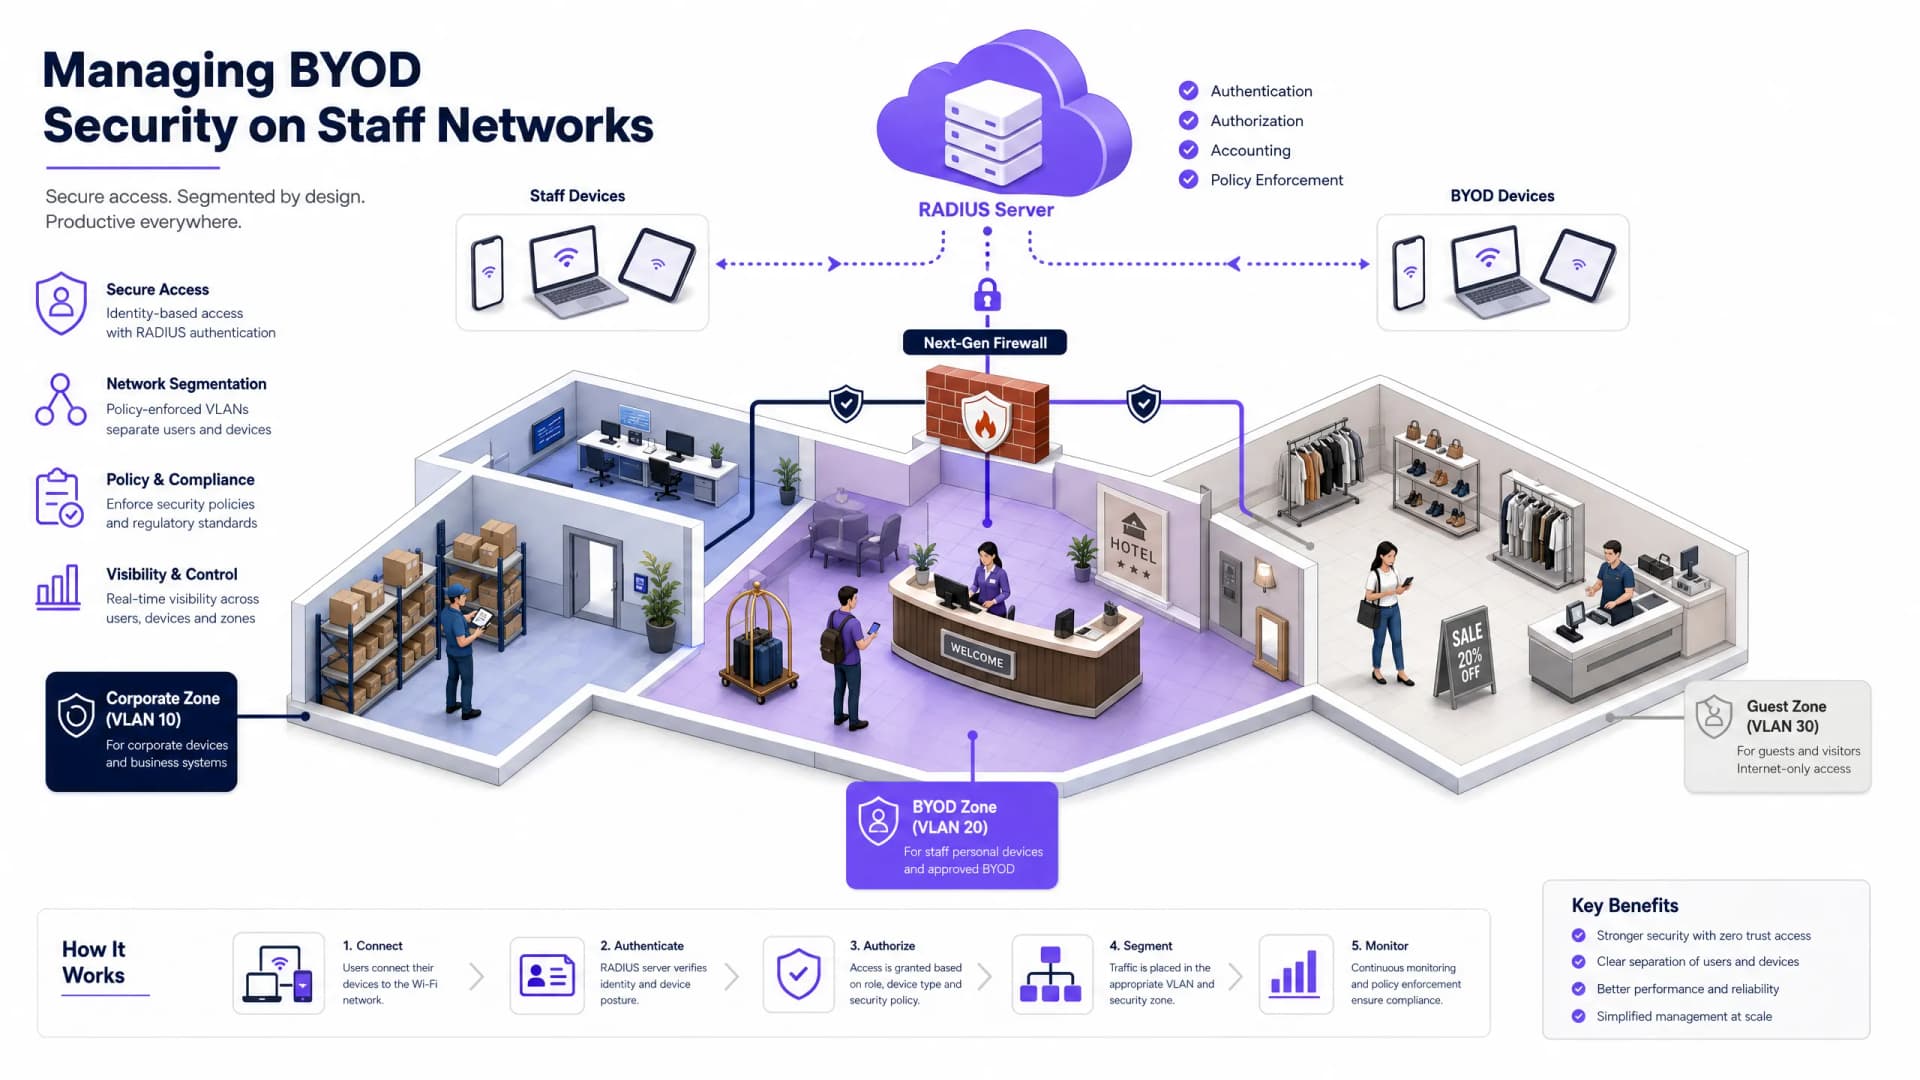
Managing BYOD (Bring Your Own Device) Security on Staff Networks
Staff WiFi

Managing BYOD (Bring Your Own Device) Security on Staff Networks

An authoritative, technical reference guide for enterprise IT managers and network architects on securing Bring Your Own Device (BYOD) access on staff networks. This guide outlines the exact network architecture, authentication protocols, and MDM integration workflows required to mitigate data leakages and maintain regulatory compliance across high-footfall venues.

9 mins read2k words
Mitigating Rogue Access Points on Enterprise Networks
Staff WiFi

Mitigating Rogue Access Points on Enterprise Networks

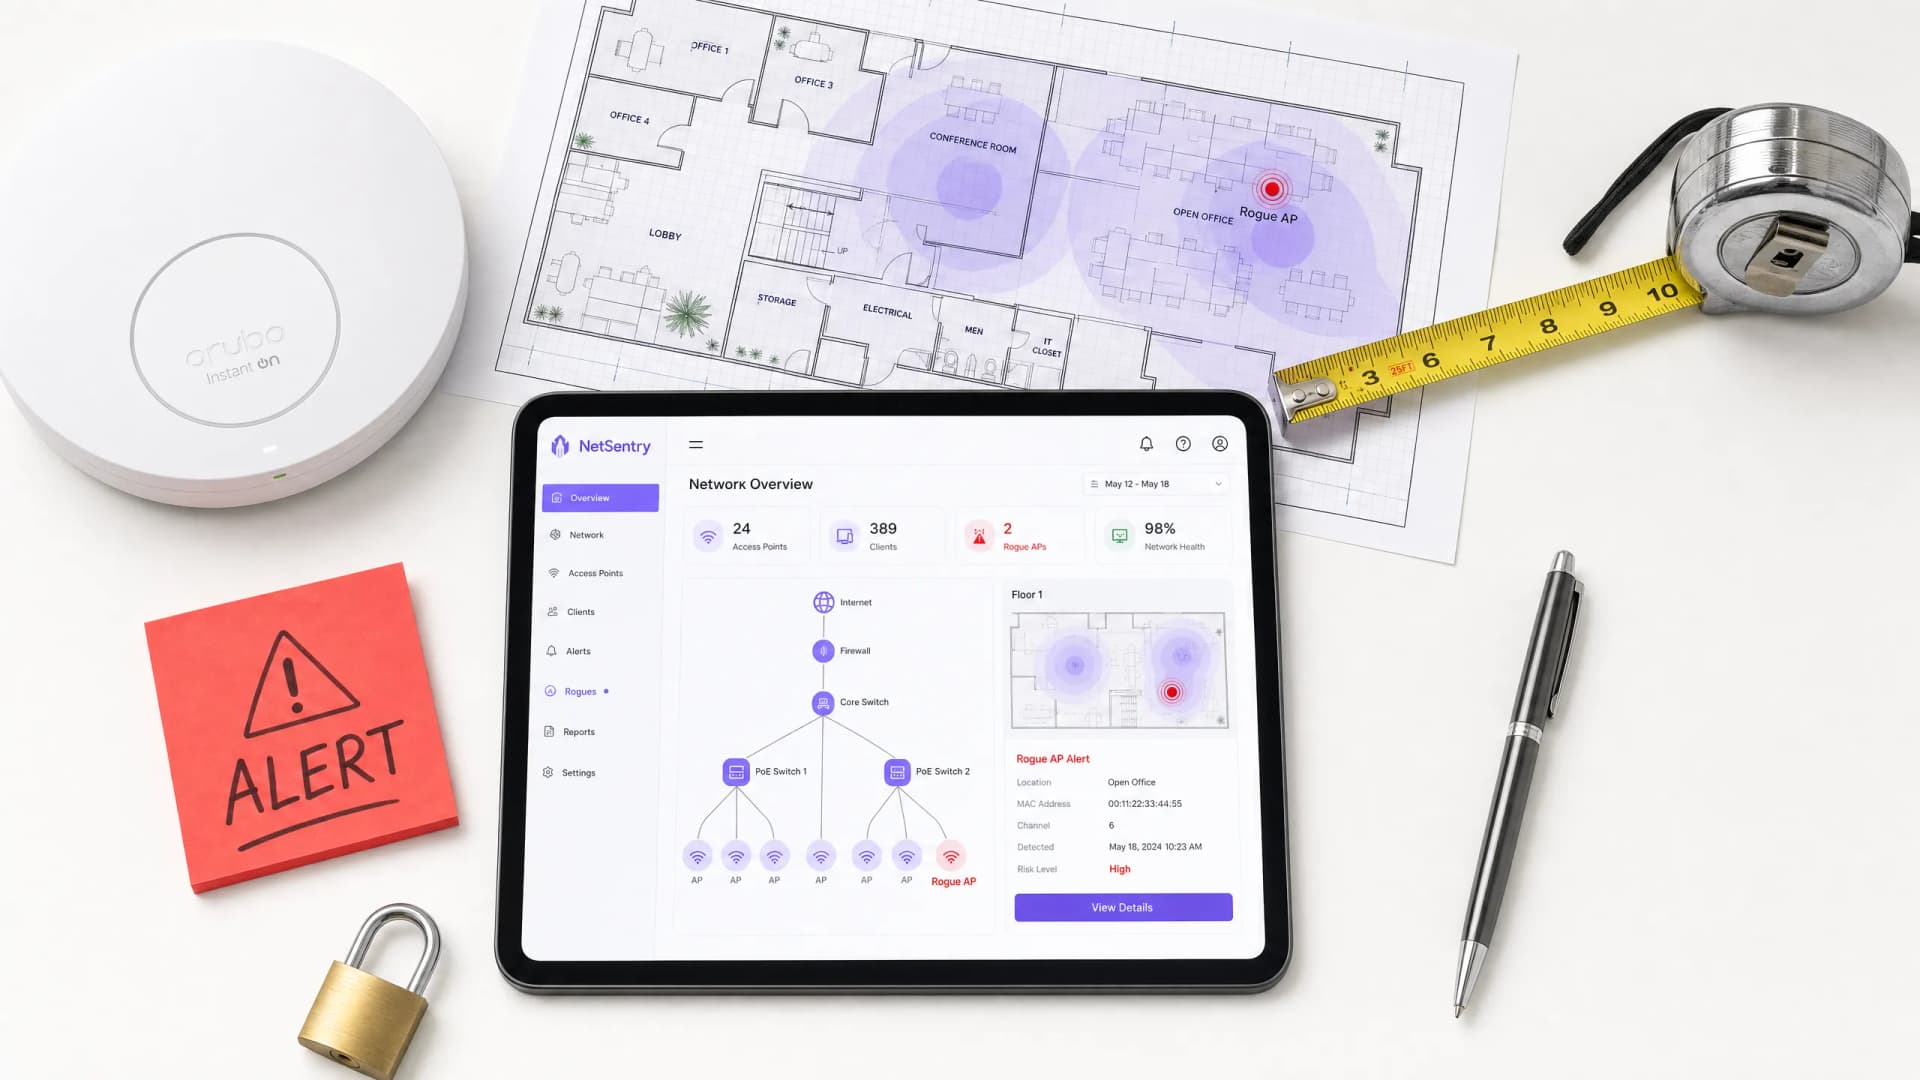
This technical reference guide details the architecture, deployment, and operational procedures for mitigating rogue access points on enterprise networks using Wireless Intrusion Prevention Systems (WIPS) and Wireless Intrusion Detection Systems (WIDS). It provides actionable frameworks for IT security administrators to detect, classify, and neutralise unauthorised APs across complex physical environments including hospitality, retail, healthcare, and public-sector venues. The guide covers threat classification, automated containment mechanisms, compliance implications (PCI DSS, GDPR, HIPAA), and measurable business outcomes.

9 mins read2k words
802.1X Authentication Explained for Corporate Networks
Staff WiFi

802.1X Authentication Explained for Corporate Networks

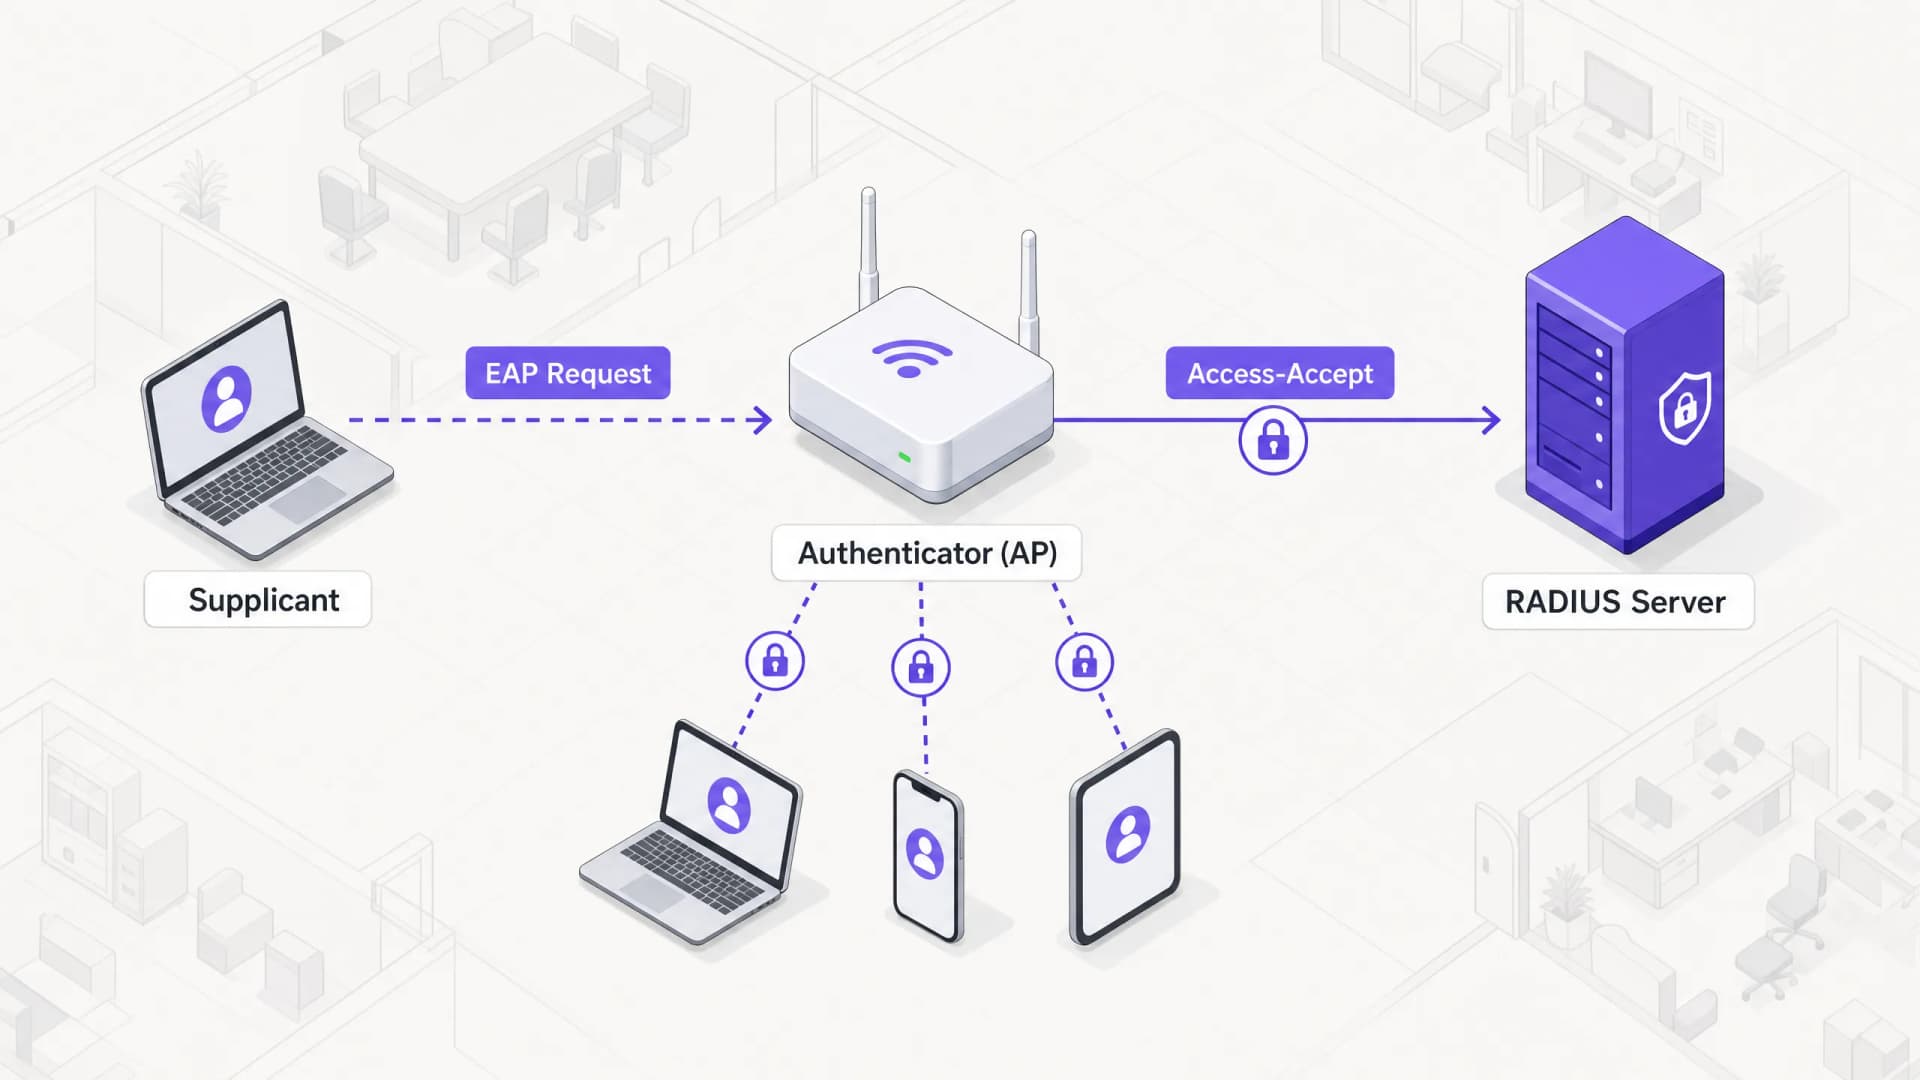
This authoritative guide provides IT leaders and network architects with a deep technical breakdown of 802.1X authentication for corporate networks. It covers architecture, EAP methods, deployment strategies, and risk mitigation to ensure secure, compliant WiFi access across multi-site environments.

6 mins read1k words
Secure BYOD Policies for Staff WiFi Networks
Staff WiFi

Secure BYOD Policies for Staff WiFi Networks

This authoritative guide provides IT leaders with a vendor-neutral framework for securely onboarding staff personal devices. It details the critical architecture decisions - including network segmentation, EAP-TLS authentication, and MDM integration - required to support BYOD without compromising core corporate infrastructure.

6 mins read1k words