Technical WiFi guides
Deep, expert-led technical guides on guest WiFi, analytics, captive portals, and venue technology.
Ready to move from research to rollout? See how Purple's captive portal software handles branded guest sign-in, analytics, and compliance in one platform.
54 guides in Security
CIPA compliance: compliance checklist for venue operators
You will be able to decide whether CIPA binds your WiFi, then segment networks, route DNS through Purple Shield and close bypass routes. You will also know what evidence to keep for Form 486 or Form 479 certification. The checklist assigns every requirement an owner, so your next funding year certification has nothing missing.
WPA3 transition mode connection failures: a deployment checklist for Cisco Meraki, HPE Aruba and Ruckus
Use this checklist to diagnose why devices fail on a WPA3 SAE transition mode SSID and fix it on Cisco Meraki, HPE Aruba or Ruckus. You will match 802.11 status codes to causes, isolate PMF, 802.11r and 6GHz issues, and decide when to move to a WPA3-only SSID.
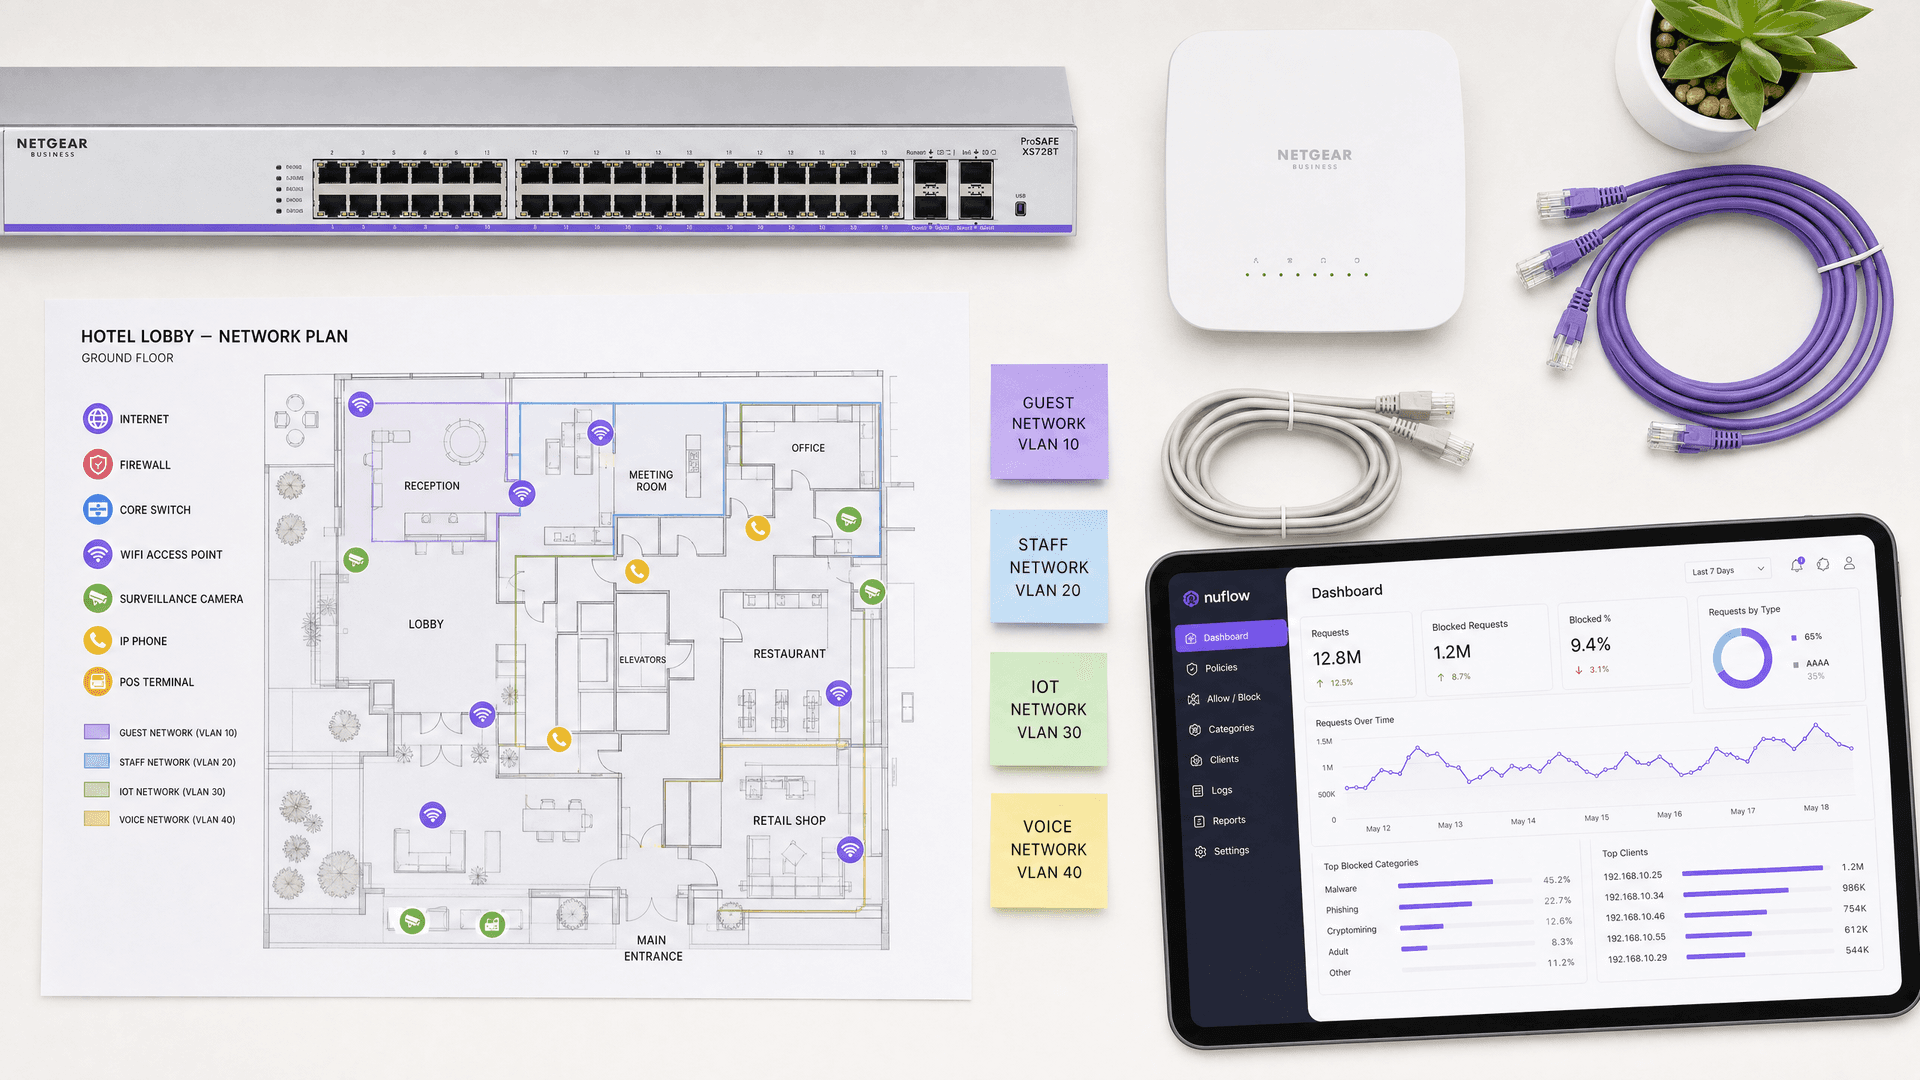
Best DNS filtering: a comprehensive guide for businesses
This technical reference guide explains how enterprise DNS filtering secures public networks by blocking malicious domains at the resolution layer - before a connection is ever established. It gives IT directors, network architects, and venue operations teams the deployment architecture, firewall configuration, and compliance context they need to protect Guest WiFi across hospitality, retail, and public-sector environments. Purple Shield blocks malware, botnets, and inappropriate content at the DNS level across 80,000+ live venues.
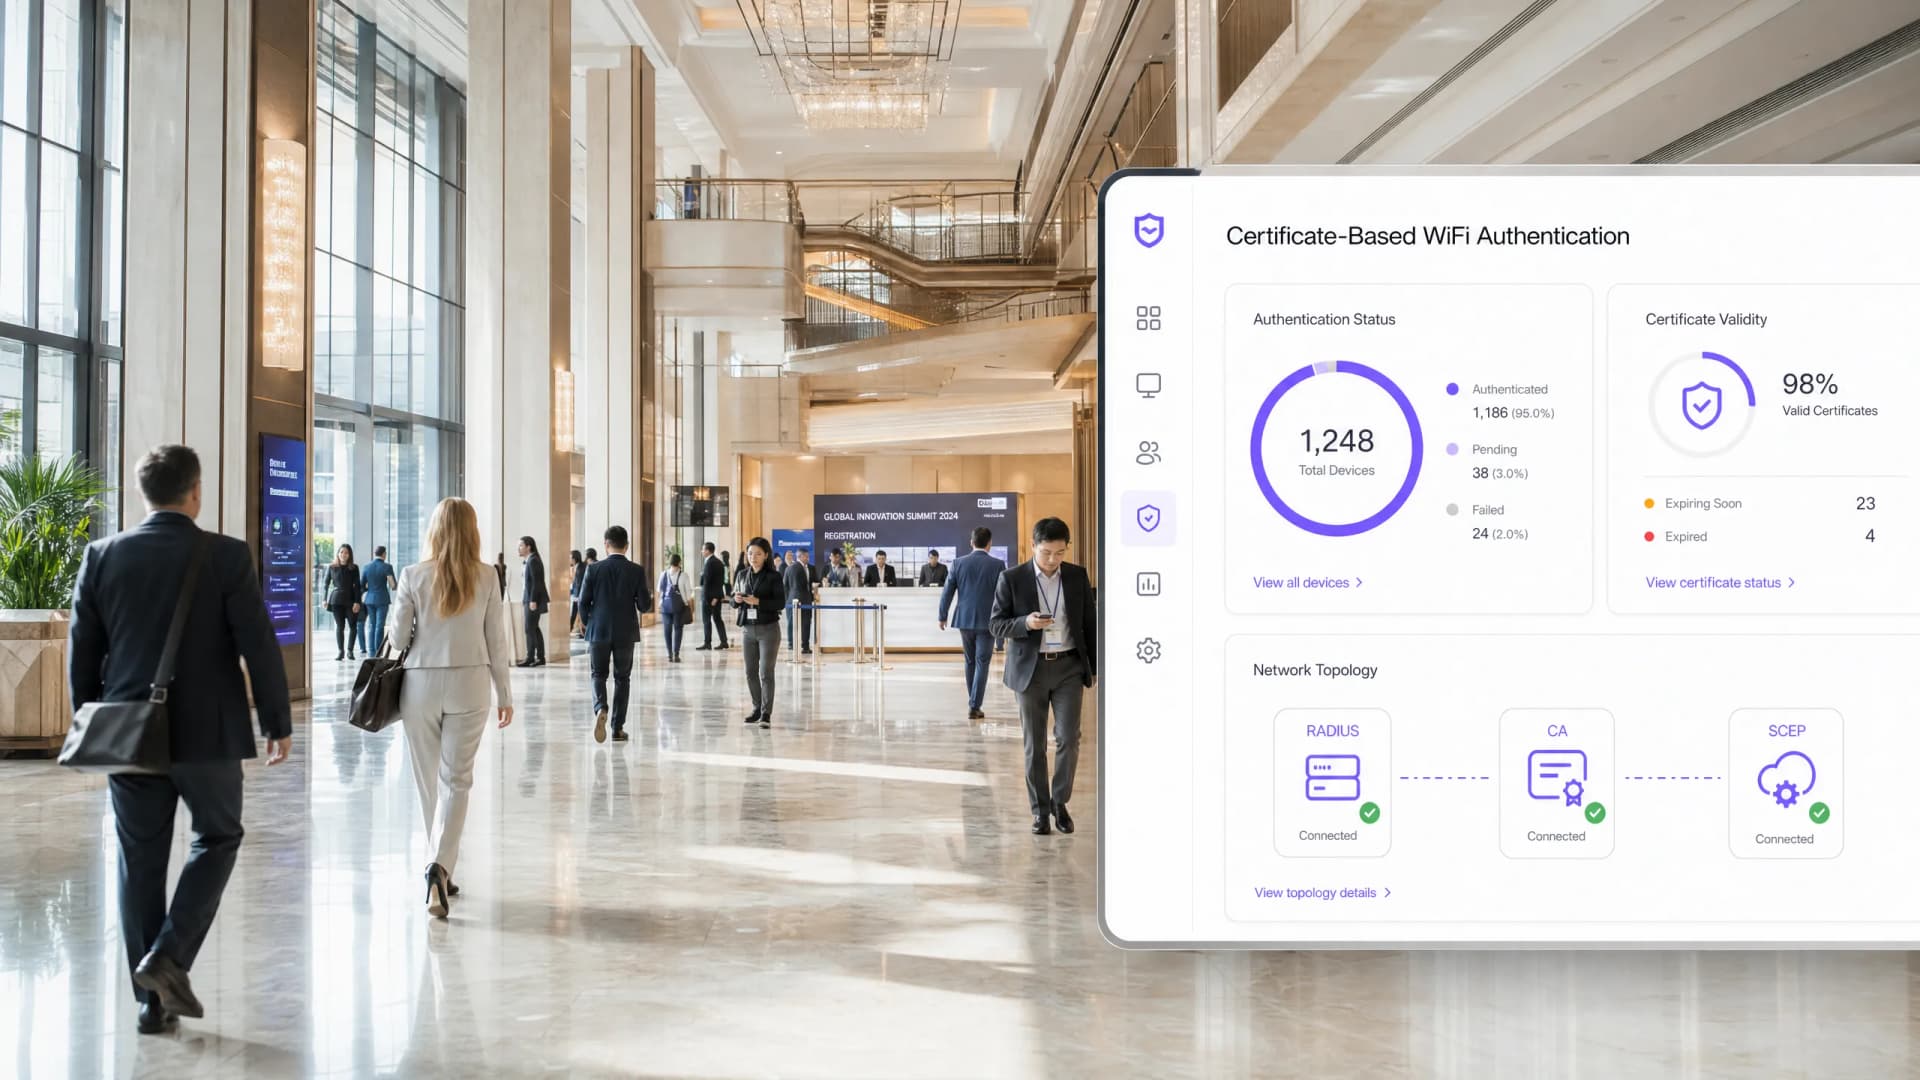
The Enterprise Guide to SCEP: Deploying Simple Certificate Enrollment Protocol for Automated Campus WiFi Security
This technical reference guide provides a definitive architectural blueprint and step-by-step implementation strategy for enterprise WiFi certificate deployment using SCEP. It covers the critical differences between SCEP and PKCS, the exact deployment sequence required for success, and real-world risk mitigation strategies for IT leaders.
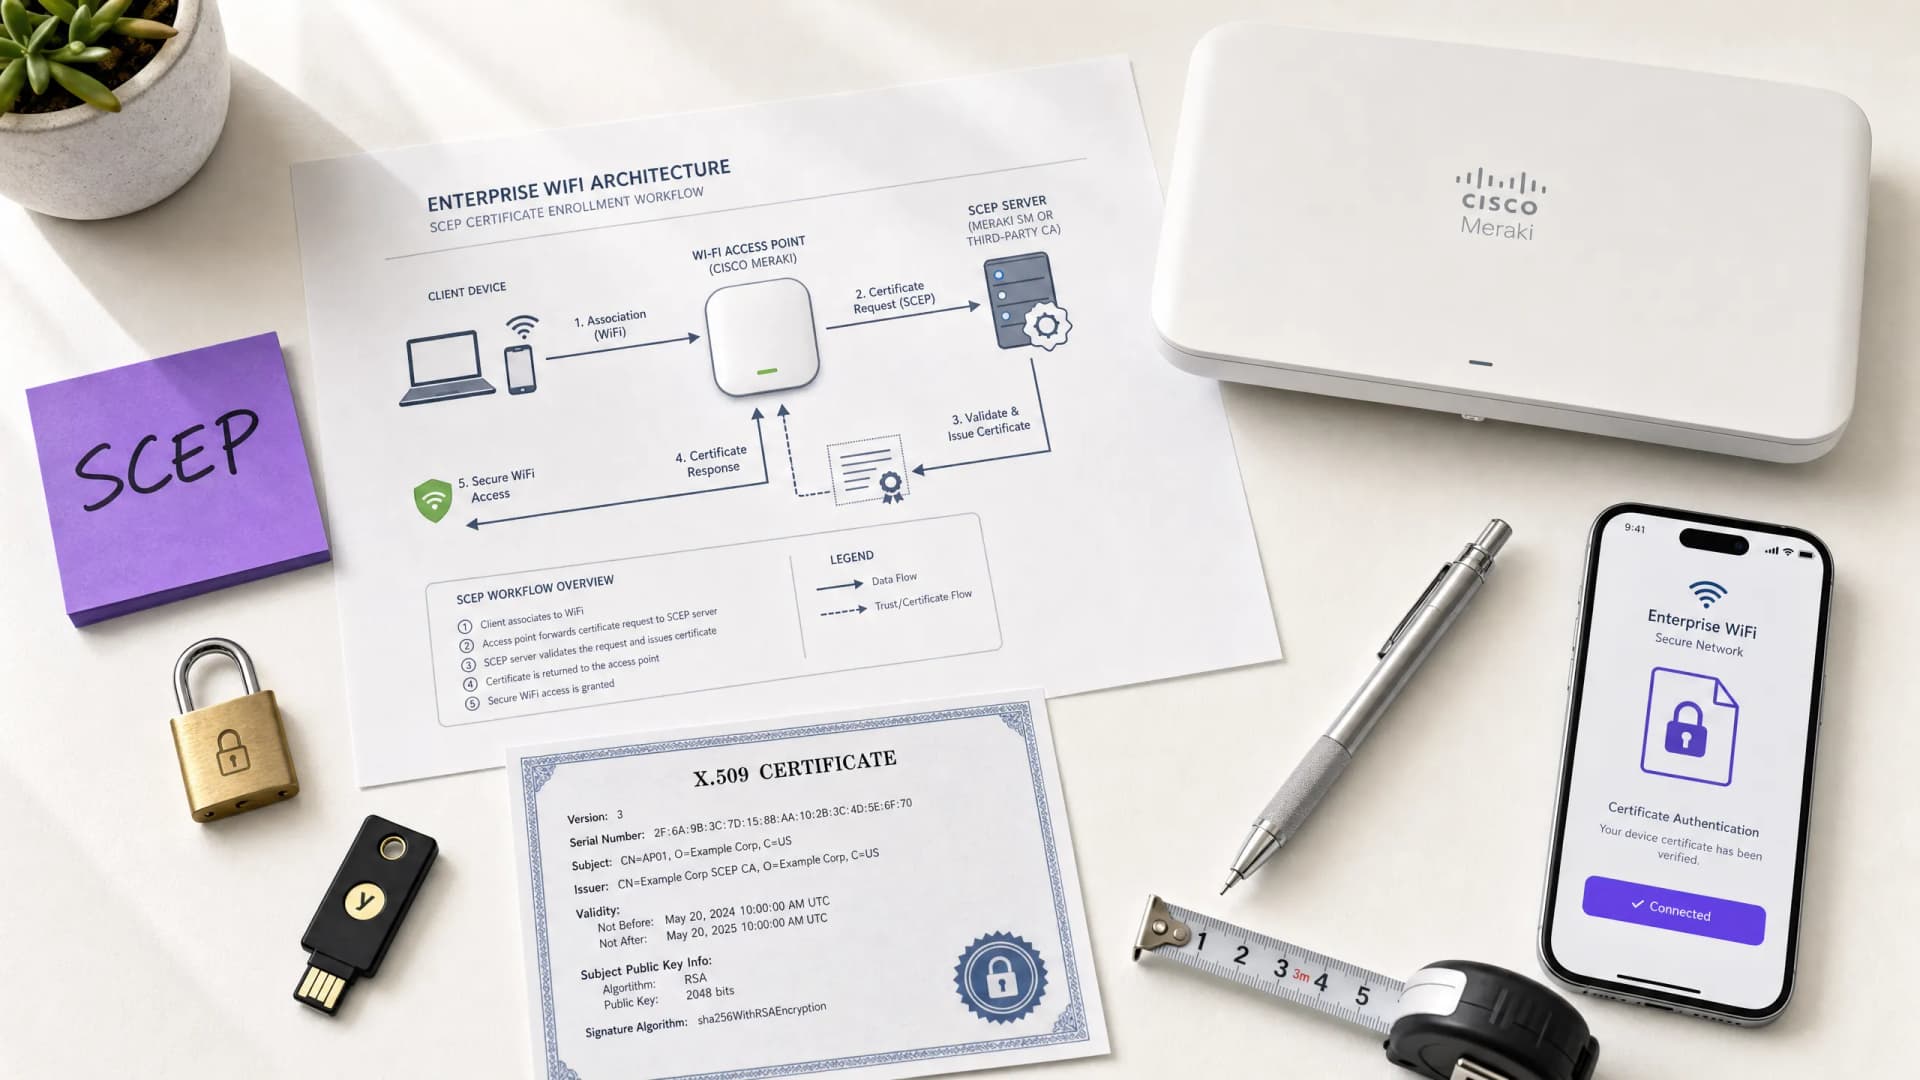
How to Implement SCEP for Automated WiFi Certificate Enrollment
This guide explains how to implement SCEP (Simple Certificate Enrollment Protocol) for automated WiFi certificate enrollment across enterprise venues. It covers the full architectural blueprint - from PKI design and MDM integration to the mandatory three-step deployment sequence - and shows IT managers and network architects how to eliminate shared credentials, automate certificate lifecycle management, and satisfy PCI DSS and GDPR requirements at scale.
Understanding Cisco SUDI: Hardware-Based Device Identity in Network Access Control
This guide details the technical architecture of Cisco SUDI, explaining how hardware-anchored identity secures network access control. It provides actionable implementation steps for IT leaders to deploy 802.1X EAP-TLS authentication and automate Zero Touch Provisioning across enterprise venues.
How to Configure SCEP for Secure BYOD and 802.1X Network Authentication
This guide provides a comprehensive technical reference for configuring SCEP to deploy certificate-based 802.1X network authentication. It covers the architectural shift from shared passwords to EAP-TLS, Mobile Device Management integration, and strict network segmentation for secure BYOD access in enterprise environments.
Staff WiFi Terms and Conditions: Legal and Compliance Essentials
This guide covers the legal and technical essentials of drafting and enforcing staff WiFi terms and conditions for enterprise venues. It details what to include in an Acceptable Use Policy (AUP), how to meet GDPR and PCI DSS requirements, and how to deploy identity-based authentication and network segmentation to protect corporate assets. IT managers, HR teams, and operations directors at hotels, retail chains, stadiums, and public-sector organisations will find actionable guidance they can implement this quarter.
Staff WiFi Policies for Retail: Securing Back-of-House Networks
This guide covers the critical technical and policy requirements for securing retail back-of-house WiFi networks - from VLAN segmentation and PCI DSS 4.0 compliance to managing employee BYOD on the shop floor. It gives IT managers, network architects, and operations directors a practical, vendor-neutral blueprint they can act on this quarter.
Enterprise SCEP Setup Guide: Certificate-Based WiFi Authentication for Higher Education and Large Networks
This guide provides a comprehensive technical blueprint for deploying certificate-based WiFi authentication using SCEP. It covers the architectural transition from pre-shared keys to EAP-TLS, deployment sequences across MDM platforms, and critical risk mitigation strategies for large-scale networks.
The Future of WiFi Security: AI-Driven NAC and Threat Detection
This authoritative guide explores the evolution of enterprise WiFi security from legacy WPA2 to AI-driven Network Access Control (NAC) and threat detection. Designed for IT leaders, it provides actionable deployment strategies for securing high-density environments like retail, hospitality, and stadiums using Purple's identity-based networks.
Managing IoT Device Security with NAC and MPSK
This technical guide details how enterprise venues can secure headless IoT devices using Multiple Pre-Shared Key (MPSK) architecture and Network Access Control (NAC). It provides actionable implementation steps for achieving micro-segmentation, containing security blast radii, and maintaining compliance without sacrificing scalability.
RadSec: How RADIUS over TLS Improves WiFi Authentication Security
This authoritative technical reference explains how RadSec (RFC 6614) secures enterprise WiFi authentication by wrapping traditional RADIUS traffic in TLS encryption. Designed for IT managers and network architects, it covers architecture, deployment strategies, and practical steps to mitigate the risks of unencrypted UDP RADIUS traffic across corporate and guest networks.
Airport WiFi Security: How to Protect Passengers on Public Networks
This technical reference guide details the specific threat landscape of airport WiFi, covering Evil Twin access points, rogue hardware, and Man-in-the-Middle attacks. It provides IT managers, network architects, and venue operations directors with actionable architectural strategies - including WPA3 implementation, VLAN segmentation, WIPS deployment, and GDPR-compliant captive portal design - to protect passengers and enterprise infrastructure at scale. Purple's guest WiFi and analytics platform is mapped concretely to each problem domain throughout.
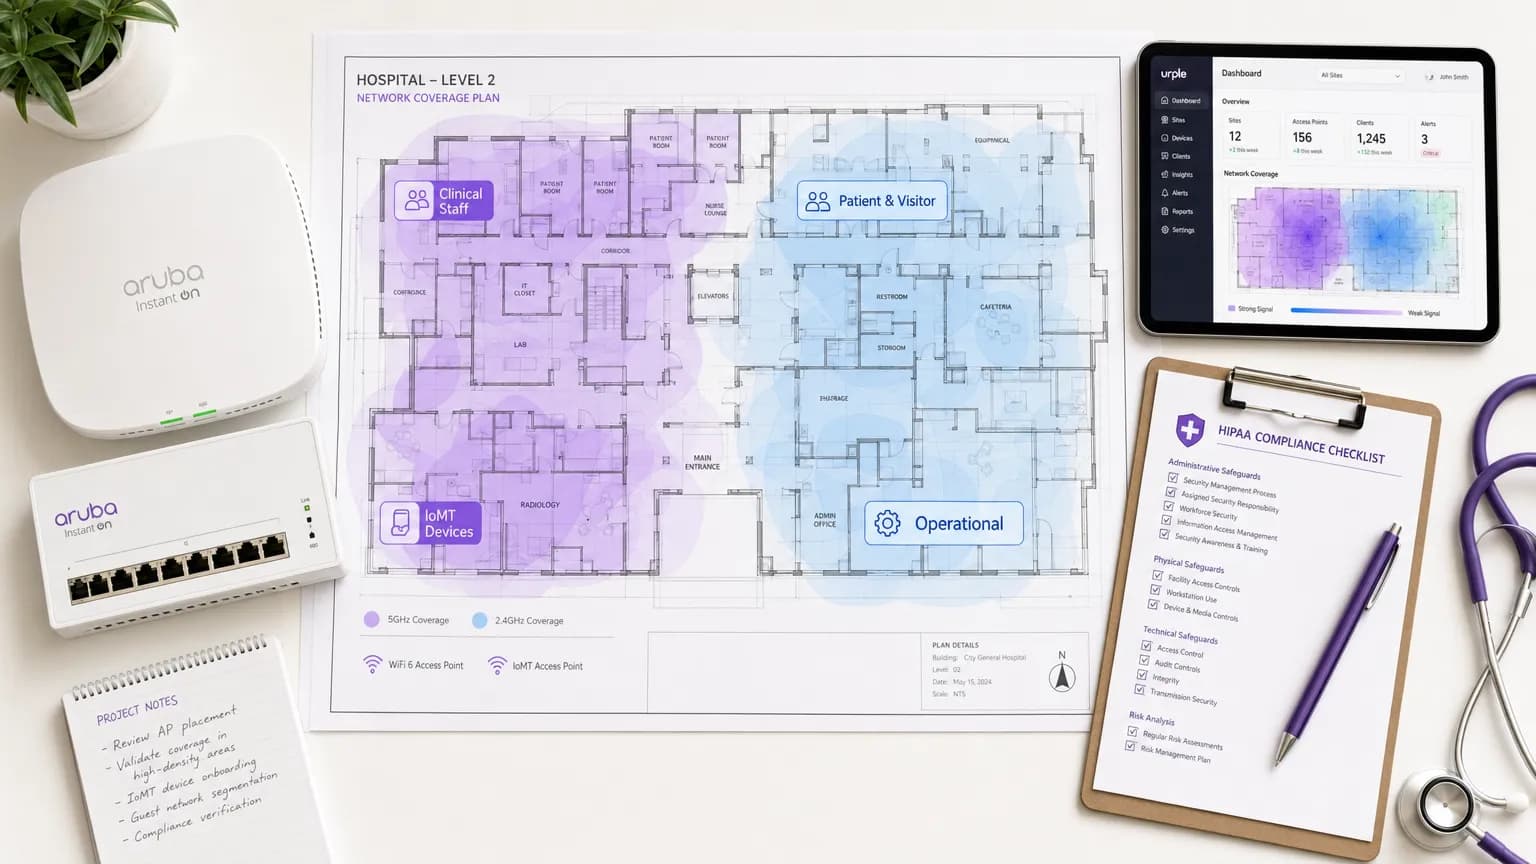
Healthcare WiFi: HIPAA, DSPT and WiFi Compliance Explained
This guide provides a definitive technical reference for IT managers, network architects, and compliance officers deploying wireless networks in healthcare environments. It maps the specific requirements of HIPAA (US) and the NHS Data Security and Protection Toolkit (DSPT, UK) to concrete network architecture decisions - covering segmentation, identity-based access, encryption standards, and IoMT device handling. Purple's guest WiFi and analytics platform is positioned throughout as a compliant, enterprise-grade solution for managing patient and visitor connectivity within a governed wireless estate.
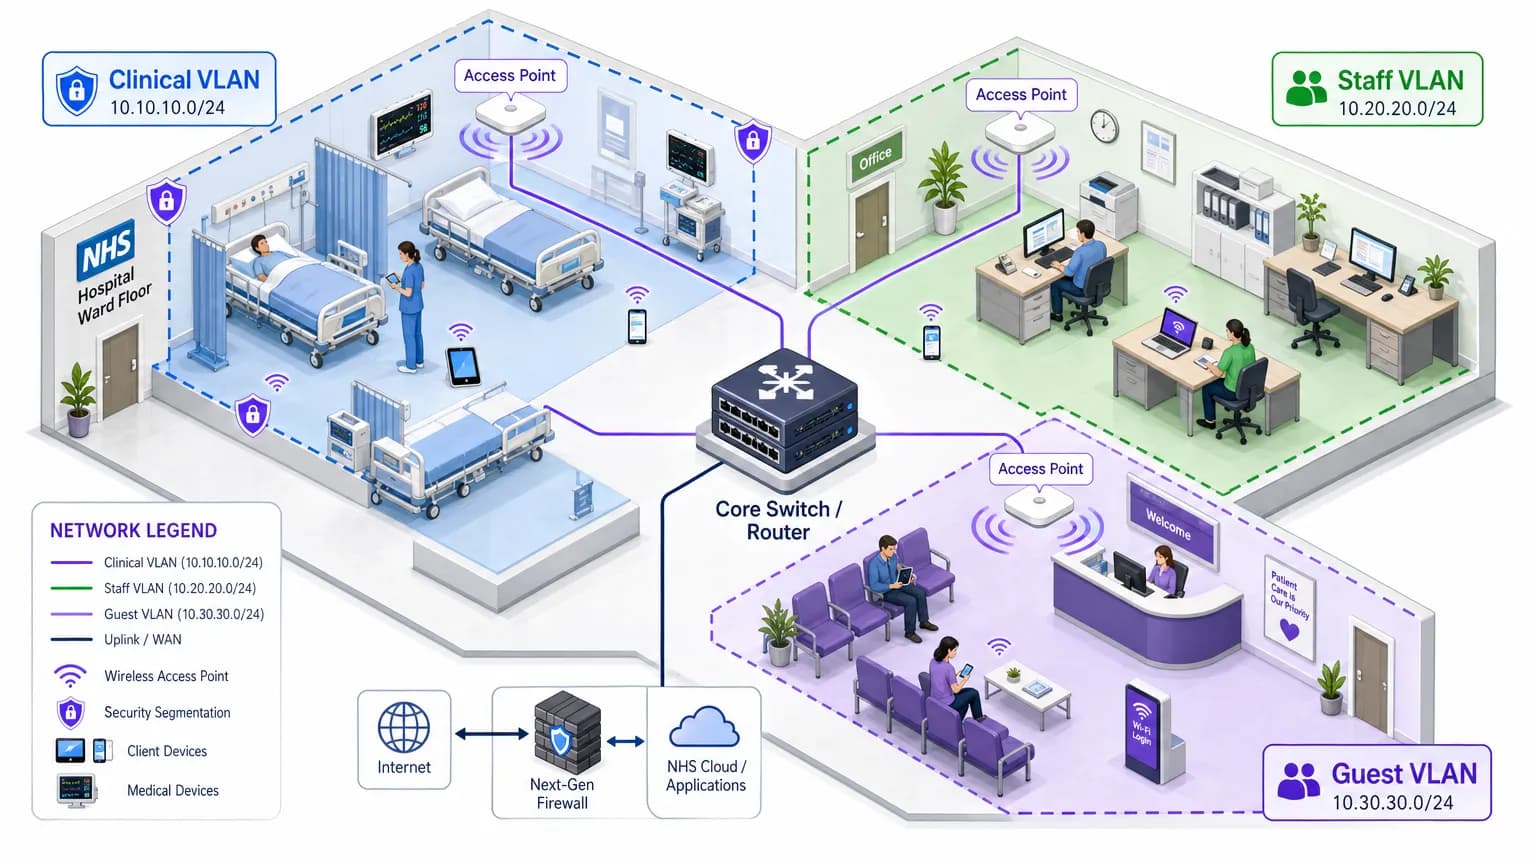
NHS Staff WiFi: How to Deploy Secure Wireless Networks in Healthcare
This technical reference guide details the architecture, security protocols, and deployment strategies for NHS Staff WiFi, covering 802.1X authentication, VLAN segmentation, BYOD policies, and DSP Toolkit compliance. It provides actionable guidance for IT leaders on deploying enterprise-grade wireless networks that serve clinical, administrative, and guest users on shared physical infrastructure without compromising security. Whether you are planning a new deployment or hardening an existing estate, this guide delivers the decision frameworks and implementation steps needed to act this quarter.
Hotel WiFi Security: How to Protect Your Guests and Your Reputation
This authoritative guide provides IT managers and venue operations directors with a comprehensive framework for securing hotel WiFi networks. It covers essential technical implementations including network segmentation, robust authentication protocols, and compliance-driven captive portals to protect guest data and safeguard the venue's reputation.

How to Protect Customer Data Collected via WiFi
This guide provides IT managers, network architects, and venue operations directors with a definitive technical reference for protecting customer data collected through guest WiFi deployments. It covers the full security stack - from WPA3 encryption and IEEE 802.1X access control through to GDPR-compliant consent flows, vendor due diligence, and breach notification obligations. Organisations operating in hospitality, retail, events, and public-sector environments will find actionable deployment guidance, real-world case studies, and measurable risk mitigation frameworks to implement this quarter.

India DPDP Act: Guest WiFi Compliance for Indian Venues
This authoritative technical reference guide unpacks the Digital Personal Data Protection (DPDP) Act 2023 for Indian venues operating guest WiFi. It provides actionable compliance strategies, architectural considerations for captive portals, and practical frameworks for data retention and cross-border transfers.

Brazil LGPD and Guest WiFi: A Compliance Guide
This technical reference guide details how Brazil's LGPD applies to enterprise guest WiFi deployments, focusing on captive portal compliance, lawful bases for processing, and the intersection with the Marco Civil da Internet. It provides actionable implementation guidance for IT leaders and network architects to mitigate regulatory risk while maintaining network utility.

EU AI Act and Guest WiFi: What Marketers Need to Know
The EU AI Act (Regulation 2024/1689) introduces a risk-based framework that directly affects how venue operators deploy AI-driven WiFi marketing, captive portals, and guest analytics. This guide maps the Act's four risk tiers against real-world Guest WiFi use cases, identifies prohibited practices including emotion inference and social scoring, and provides actionable compliance steps for IT teams and marketing directors operating across hospitality, retail, events, and public-sector environments. Understanding where your deployment sits on the risk spectrum - and implementing the Article 50 transparency obligations for AI chatbots and conversational portals - is no longer optional: prohibited practice enforcement began in February 2025.

PIPEDA Compliance for Guest WiFi in Canada
This guide provides a definitive technical and operational reference for Canadian venue operators deploying guest WiFi under PIPEDA. It covers the OPC's meaningful consent framework, the accountability principle, enforcement precedents from the Tim Hortons and Google WiFi investigations, and the architectural changes required to meet the incoming Consumer Privacy Protection Act (CPPA) under Bill C-27. IT managers and compliance leads will find actionable captive portal design specifications, data minimisation requirements, and a clear roadmap for future-proofing against GDPR-scale penalties.

Is University WiFi Safe? A Guide for Students
A comprehensive technical reference for IT managers and venue operators on the security architecture of university WiFi (eduroam/802.1X). This guide unpacks how enterprise-grade authentication works, its implementation pitfalls, and how these principles apply to hospitality, retail, and public sector deployments.

Is Train WiFi Safe? What Rail Passengers Need to Know
This guide examines the security architecture of passenger rail WiFi networks, dissecting the threat landscape from packet sniffing and Evil Twin attacks to Man-in-the-Middle exploits. It provides actionable deployment guidance for operators and corporate IT teams, covering client isolation, captive portal authentication, DNS filtering, and the path to Hotspot 2.0 - with direct integration points for Purple's Guest WiFi and analytics platform.
Got questions about your specific setup?
Our team works with venue operators, IT managers, and network engineers across 80,000 venues. Book a 20-minute call and we will show you how others like you solved it.