
Technical WiFi guides
Deep, expert-led technical guides on guest WiFi, analytics, captive portals, and venue technology.
Ready to move from research to rollout? See how Purple's captive portal software handles branded guest sign-in, analytics, and compliance in one platform.
63 guides in Security

EU AI Act and Guest WiFi: What Marketers Need to Know
The EU AI Act (Regulation 2024/1689) introduces a risk-based framework that directly affects how venue operators deploy AI-driven WiFi marketing, captive portals, and guest analytics. This guide maps the Act's four risk tiers against real-world Guest WiFi use cases, identifies prohibited practices including emotion inference and social scoring, and provides actionable compliance steps for IT teams and marketing directors operating across hospitality, retail, events, and public-sector environments. Understanding where your deployment sits on the risk spectrum - and implementing the Article 50 transparency obligations for AI chatbots and conversational portals - is no longer optional: prohibited practice enforcement began in February 2025.

PIPEDA Compliance for Guest WiFi in Canada
This guide provides a definitive technical and operational reference for Canadian venue operators deploying guest WiFi under PIPEDA. It covers the OPC's meaningful consent framework, the accountability principle, enforcement precedents from the Tim Hortons and Google WiFi investigations, and the architectural changes required to meet the incoming Consumer Privacy Protection Act (CPPA) under Bill C-27. IT managers and compliance leads will find actionable captive portal design specifications, data minimisation requirements, and a clear roadmap for future-proofing against GDPR-scale penalties.

Is Supermarket WiFi Safe? A Shopper's Guide
This authoritative guide examines the technical realities of supermarket WiFi safety, providing actionable architecture and security strategies for IT leaders in the retail sector. It details the threat landscape - from Evil Twin APs to Man-in-the-Middle attacks - alongside the mitigation stack required to protect consumers and enterprise operations. Retailers and venue operators will find concrete implementation guidance covering VLAN segmentation, client isolation, WPA3, PCI DSS compliance, and GDPR-compliant guest onboarding via platforms like Purple.

Is University WiFi Safe? A Guide for Students
A comprehensive technical reference for IT managers and venue operators on the security architecture of university WiFi (eduroam/802.1X). This guide unpacks how enterprise-grade authentication works, its implementation pitfalls, and how these principles apply to hospitality, retail, and public sector deployments.

Is Train WiFi Safe? What Rail Passengers Need to Know
This guide examines the security architecture of passenger rail WiFi networks, dissecting the threat landscape from packet sniffing and Evil Twin attacks to Man-in-the-Middle exploits. It provides actionable deployment guidance for operators and corporate IT teams, covering client isolation, captive portal authentication, DNS filtering, and the path to Hotspot 2.0 - with direct integration points for Purple's Guest WiFi and analytics platform.

Is Hospital WiFi Safe? What Patients and Visitors Should Know
This comprehensive technical reference guide examines the security architecture of hospital guest WiFi networks. It provides IT managers and venue operators with actionable implementation strategies, focusing on network segmentation, encryption standards, and compliance frameworks to ensure patient data remains protected without compromising clinical operations.

Is Café and Coffee Shop WiFi Safe?
This authoritative technical guide examines the real security risks of café and coffee shop WiFi for both consumers and venue operators, covering threat vectors including Evil Twin attacks, packet sniffing, and client-to-client exploits. It provides IT managers and network architects with a practical, standards-referenced deployment framework - from VLAN segmentation and WPA3 migration to captive portal implementation and GDPR-compliant analytics. Purple's Guest WiFi and analytics platform is positioned as a concrete solution across hospitality, retail, and public-sector environments.

Is Airport WiFi Safe? A Traveller's Security Guide
This guide provides an authoritative technical reference for IT managers, network architects, and venue operations directors on the security risks of airport WiFi and how to mitigate them. It covers the full threat landscape - from Evil Twin access points to rogue DHCP servers - and delivers a practical, standards-based deployment framework using IEEE 802.1X, WPA3, and network segmentation. It also maps Purple's Guest WiFi and analytics platform to each risk vector, providing concrete integration points for operators looking to deploy secure, GDPR-compliant, and commercially viable public WiFi.

Is Hotel WiFi Safe? What Every Traveller Needs to Know
This comprehensive technical guide details the specific security risks inherent in hotel WiFi networks, including rogue APs and MITM attacks. It provides actionable, vendor-neutral implementation steps for IT managers and network architects to secure their wireless infrastructure and leverage managed guest WiFi platforms.

Is Public WiFi Safe? The Definitive Guide
This definitive guide provides enterprise IT leaders with actionable strategies for architecting secure public WiFi networks. It details the technical mitigation of primary threats like MITM attacks and rogue access points, while outlining how to leverage platforms like Purple to ensure compliance, protect corporate infrastructure, and safely monetise guest connectivity.

HIPAA-Compliant WiFi: A Guide for Healthcare Organisations
This technical reference guide provides actionable compliance strategies for healthcare IT teams deploying enterprise and guest WiFi. It covers network segmentation, 802.1X authentication, audit logging, and how to implement secure, isolated wireless access using Purple's platform.

How to Monitor WiFi Network Traffic: A Guide for IT Teams
This technical guide provides actionable strategies for monitoring enterprise WiFi traffic, focusing on architecture, security, and performance. It equips IT teams in hospitality, retail, and public sectors with the frameworks needed to deploy scalable, secure network monitoring solutions.

BYOD WiFi Security: How to Safely Let Personal Devices on Your Network
A pragmatic, vendor-neutral guide for IT leaders on securing BYOD WiFi access. It covers the implementation of 802.1X authentication, MDM integration, and strict network segmentation to protect corporate assets while enabling personal devices.

The Most Secure Method of WiFi Authentication: A Comparison
This technical reference guide provides a definitive ranked comparison of WiFi authentication methods - from the deprecated WEP standard through to EAP-TLS certificate-based authentication - helping IT managers, network architects, and CTOs at enterprise venues make informed, compliance-aligned security decisions. It covers the technical architecture of each protocol, real-world deployment scenarios in hospitality and retail, and practical implementation guidance for organisations operating under PCI DSS and GDPR obligations. For venue operators and IT teams, this guide translates complex cryptographic standards into actionable deployment decisions with measurable business outcomes.

WPA-PSK Explained: What It Is, How It Works, and Its Security Risks
This authoritative technical reference breaks down the mechanics of WPA-PSK - its 4-way handshake, cryptographic architecture, and inherent security vulnerabilities - and explains precisely why enterprise networks must transition to robust 802.1X or managed captive portal architectures. It provides actionable deployment guidance for IT leaders managing complex venue environments across hospitality, retail, events, and public-sector organisations.

What Is WiFi Security? A Complete Guide to Wireless Network Security
A comprehensive technical reference for IT leaders on securing enterprise wireless networks. This guide covers the evolution of encryption protocols, architectural best practices for segmentation, and defence strategies against common WiFi threats.

How to Set Up a Secure Guest WiFi Network: Step-by-Step
This guide provides a comprehensive technical walk-through for IT teams on designing and deploying a secure guest WiFi network from scratch. It covers VLAN segmentation, firewall rule design, captive portal integration, and bandwidth management, with real-world implementation scenarios from hospitality and retail environments. Venue operators and network architects will find actionable, vendor-neutral guidance that addresses both security and compliance requirements.

RadSec: Securing RADIUS Authentication Traffic with TLS
This comprehensive guide explores RadSec (RADIUS over TLS), detailing how it secures network authentication traffic for modern cloud and multi-site deployments. It provides network architects with practical implementation steps, certificate management strategies, and troubleshooting techniques to replace legacy UDP RADIUS.

PCI DSS Compliance for Retail WiFi Networks
This technical reference guide details the PCI DSS v4.0 requirements that apply specifically to retail WiFi networks, covering network segmentation architecture, encryption standards, authentication controls, and audit trail requirements. It provides actionable implementation guidance for IT managers and network architects who need to secure payment data while safely supporting separate guest and corporate wireless access.

HIPAA-compliant guest WiFi for healthcare providers
A practical compliance guide for healthcare IT teams deploying HIPAA guest WiFi. Learn about network segmentation, data handling, and BAA requirements.

CCPA vs GDPR: Global Privacy Compliance for Guest WiFi Data
This guide provides a comprehensive technical comparison of CCPA and GDPR requirements for guest WiFi deployments. It delivers actionable strategies for IT leaders and network architects to build a unified, dual-compliant consent framework that mitigates regulatory risk whilst preserving the commercial value of first-party data.
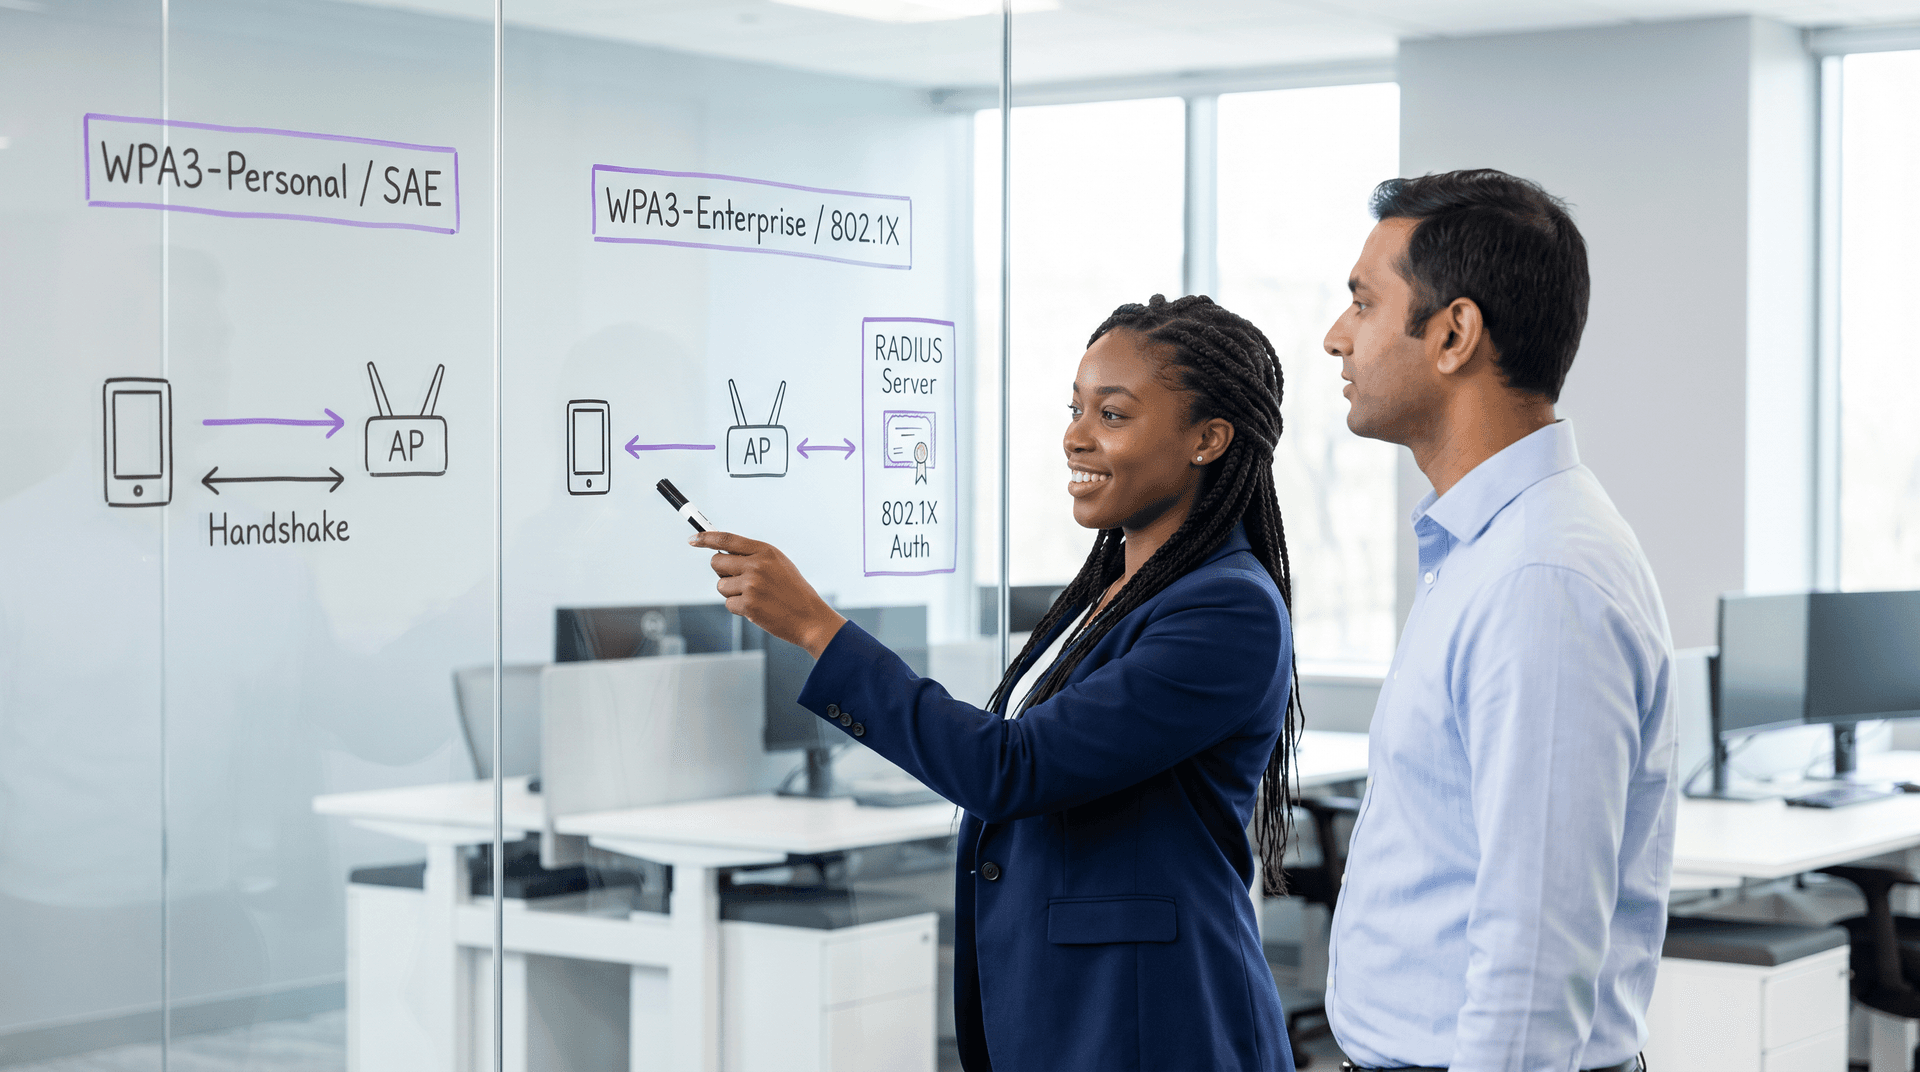
WPA3 Personal vs Enterprise: WiFi Security Comparison
Technical comparison of WPA3 Personal (SAE) vs WPA3 Enterprise (802.1X). Learn encryption differences, RADIUS authentication, and enterprise deployment steps.
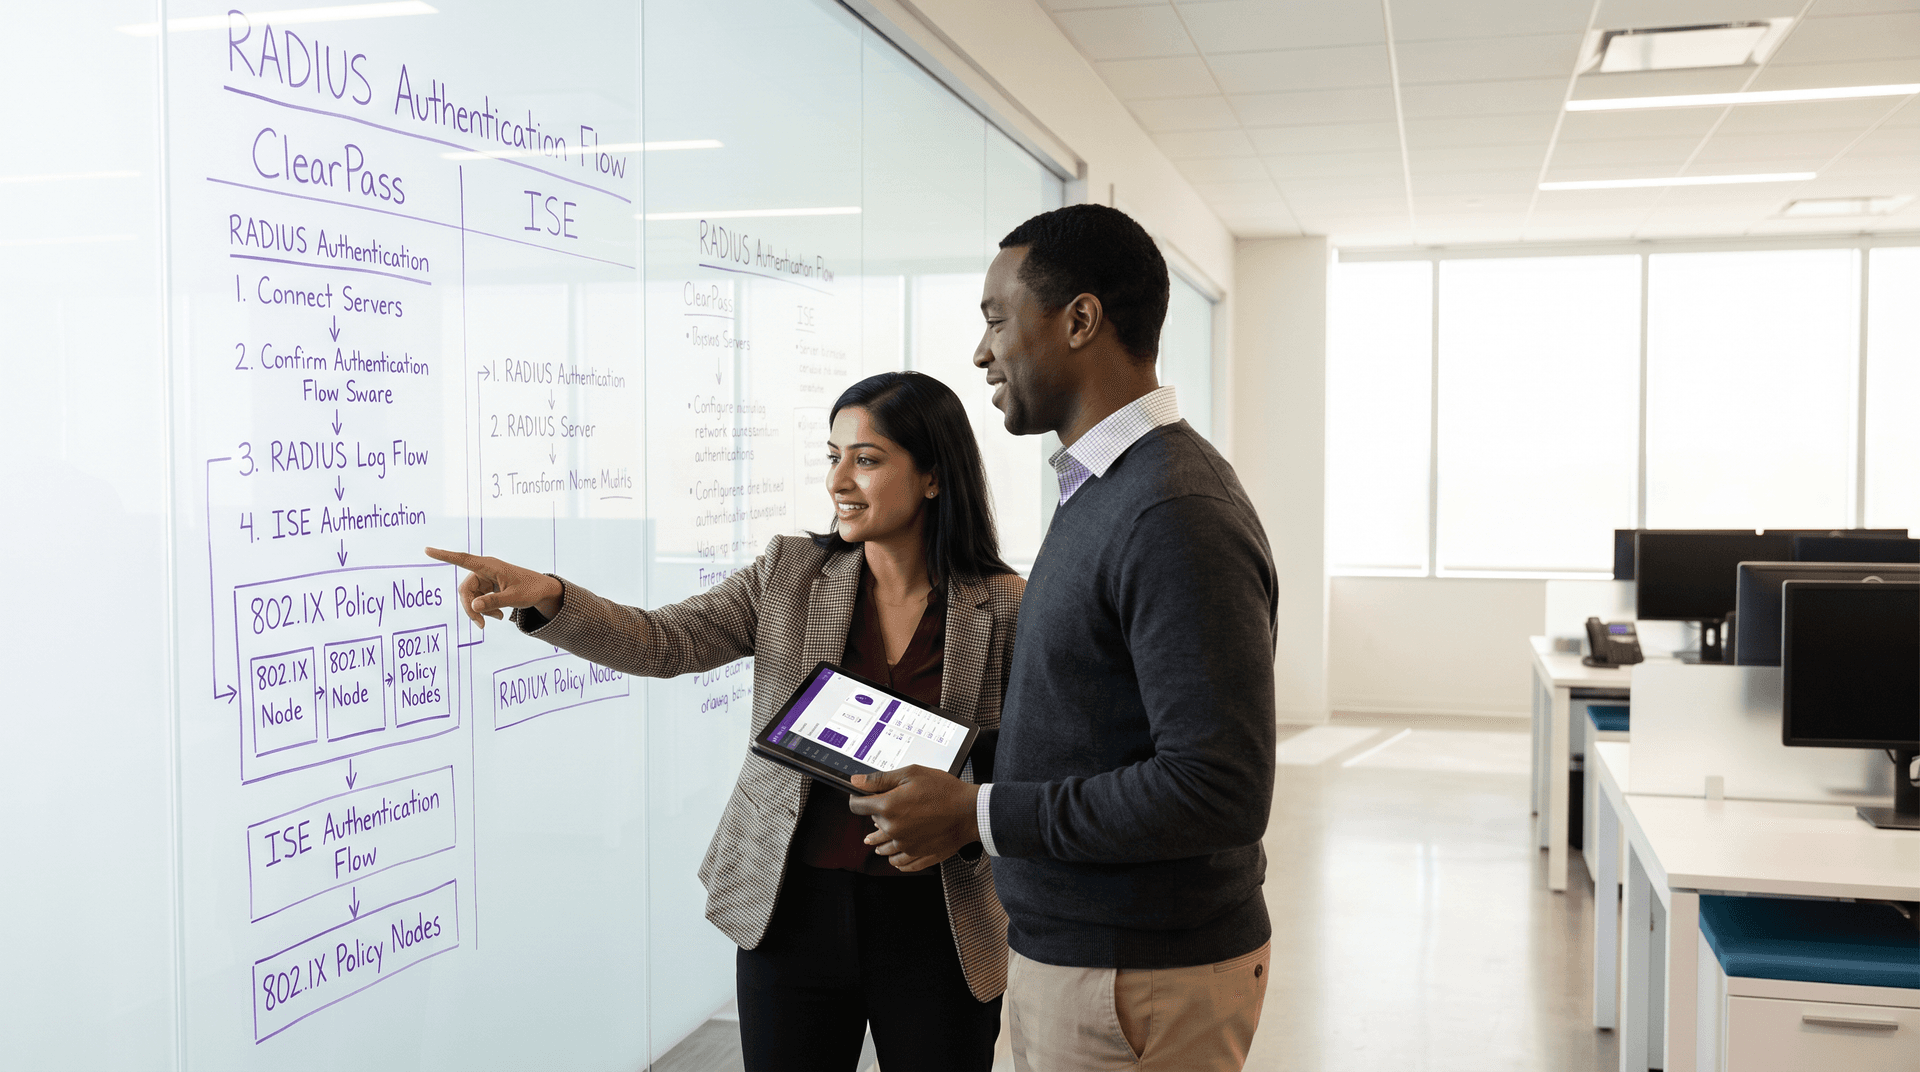
Aruba ClearPass vs Cisco ISE: enterprise NAC platform comparison
Compare Aruba ClearPass Policy Manager and Cisco ISE. Evaluate multi-vendor RADIUS AAA, 802.1X policy engines, licensing costs, and guest WiFi integration.
Rogue AP Detection: Protecting Venue WiFi from Impersonation Attacks
This guide provides a comprehensive technical reference for IT managers, network architects, and venue operations directors on deploying Wireless Intrusion Prevention Systems (WIPS) to detect and neutralise rogue access points and evil twin attacks. It covers detection methodologies, legal countermeasures, compliance requirements, and real-world implementation scenarios across hospitality, retail, and public-sector environments. Organisations that implement the strategies outlined here will strengthen their wireless security posture, reduce compliance risk, and protect both their infrastructure and their users from WiFi impersonation threats.
Got questions about your specific setup?
Our team works with venue operators, IT managers, and network engineers across 80,000 venues. Book a 20-minute call and we will show you how others like you solved it.
