Technical WiFi guides
Deep, expert-led technical guides on guest WiFi, analytics, captive portals, and venue technology.
Ready to move from research to rollout? See how Purple's captive portal software handles branded guest sign-in, analytics, and compliance in one platform.
455 guides
802.11r and 802.11k on Android: fast roaming deployment on Cisco Meraki, HPE Aruba and Ubiquiti UniFi
You will be able to decide whether to enable 802.11r, 802.11k and 802.11v for your Android fleet on Cisco Meraki, HPE Aruba or Ubiquiti UniFi, and which 802.11r strategy to run. You will also be able to pilot the change safely, confirm each handset model in a packet capture and fix the six most common association failures.
Cisco Meraki 802.11r adaptive vs enabled: fixing roaming on MR access points
You will be able to choose between disabled, enabled and adaptive 802.11r on each Cisco Meraki MR SSID, based on your device mix and security mode. You will also diagnose join failures and slow roams with a test SSID, the event log and a packet capture, then segment SSIDs by device class.
Microsoft Cloud PKI for WiFi: EAP-TLS certificate deployment with Intune and Entra ID
You will be able to decide whether Microsoft Cloud PKI, a Cloud PKI root or bring your own CA (BYOCA) fits your estate. You can then deploy EAP-TLS WiFi certificates to Intune-managed devices without NDES. The guide also covers making RADIUS trust the chain, revoking certificates through the CRL and fixing the eight most common failures.
Cloud4Wi Alternatives: Captive Portal Platforms Compared
Use this comparison to shortlist a Cloud4Wi alternative by architecture first, marketing depth second and price third. You can match your estate to Purple, IronWiFi, Cloudi-Fi, Nomadix or staying on Cloud4Wi. You can then model three-year cost and run a demonstration, exit test and 10-site pilot before you commit.
FortiGate captive portal setup with an external portal server
You will be able to configure a FortiGate to enforce an external captive portal hosted by Purple, with RADIUS authentication and accounting, a working exempt list and a trusted certificate. You can also decide between the built-in and external portal, test on real devices and fix the faults that most often block guest logins.
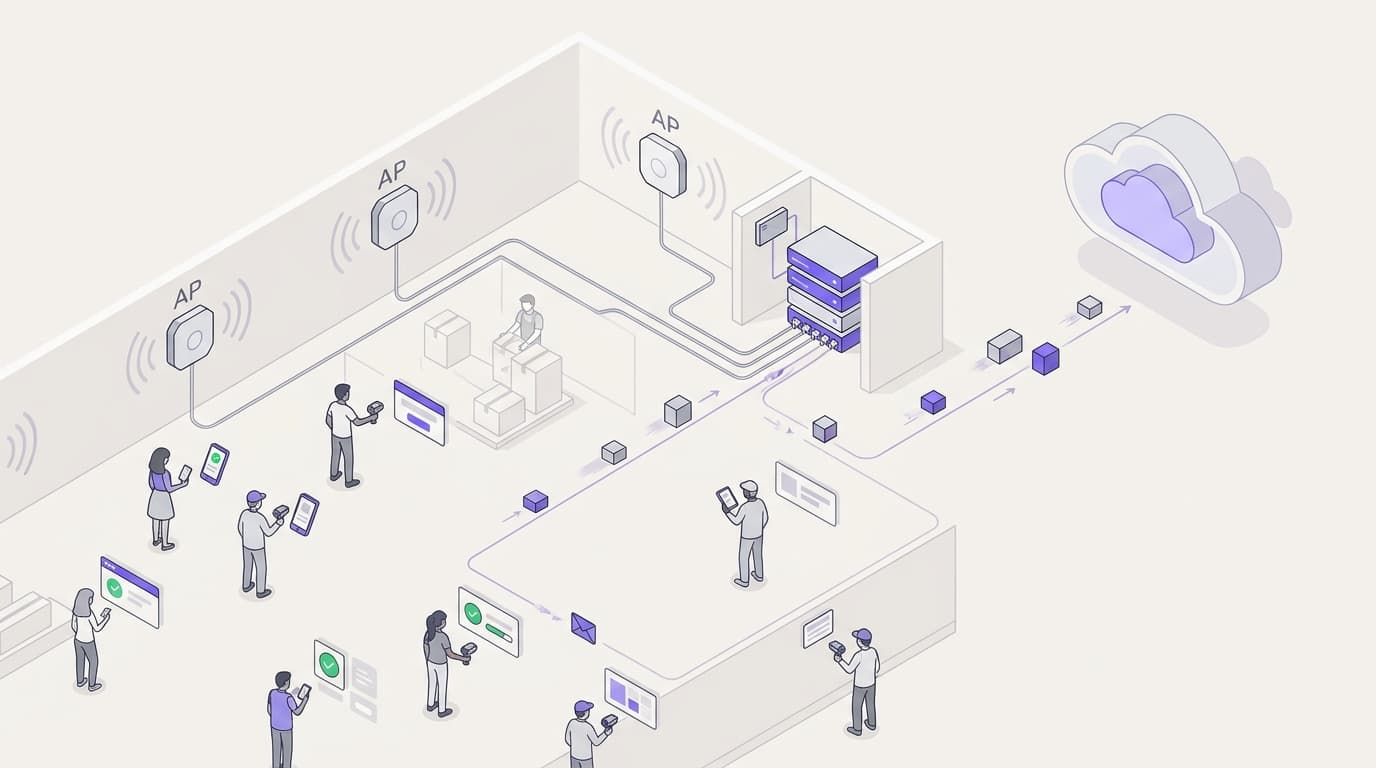
Configuring 802.1X on Juniper Mist with cloud RADIUS
You will be able to configure a WPA2 or WPA3-Enterprise WLAN on Juniper Mist that authenticates against cloud RADIUS, decide between UDP RADIUS, RadSec and a Mist Edge proxy, and map RADIUS attributes to dynamic VLANs. You will also know where Mist's client insights timeline and Marvis show exactly where a failed authentication broke.
White label captive portal software: what MSPs and resellers should check before signing
You will be able to choose between full white label, co-branded and referral models, then score vendors on multi-tenancy, branding depth, hardware coverage, billing, TCPA and CAN-SPAM consent records, APIs and support escalation. The guide ends with 15 RFP questions and a red-flag table you can send to every shortlisted vendor before you sign.

Captive portal pricing compared: per site, per access point and per user models
Decide which captive portal pricing model fits your estate: per site, per access point, per user or session, or bundled with hardware. Apply your venue count, AP count and monthly logins to every quote. Then add SMS, support, integration, compliance and exit costs, and rank vendors on a single three-year total.
Network topology mapping guide: building a live device map from CDP, LLDP, and MTR
You will be able to build a network map that stays current by merging CDP and LLDP neighbor tables, MTR path hops and a LAN subnet sweep. You can then check the map for accuracy, fix common discovery faults and decide whether a free, paid or discovery-driven mapper fits your estate.
Network device management guide: SNMP, TFTP, and syslog without a full NMS
You will be able to manage a small switch and router estate with SNMP polling, TFTP config backups and a syslog and trap receiver run from one management host. You can also decide when that lightweight setup is enough, and when continuous monitoring, trend history or multi-site scale justify a full NMS.
How Staff WiFi Helps You Meet ISO/IEC 27001: Mapping Annex A Controls to Your Wireless Network
You will be able to decide whether your staff WiFi can evidence 12 ISO/IEC 27001:2022 Annex A controls, including A.5.15, A.8.5 and A.8.22. You will also be able to replace a shared WPA2-PSK key with IEEE 802.1X and dynamic VLANs. Finally, you can assemble the RADIUS logs, segregation tests and supplier records an auditor accepts at stage 2.
Guest WiFi ROI: calculation methodology and venue benchmarks
You will be able to build a guest WiFi ROI model your finance director will sign, using gross margin and holdout groups rather than revenue and attribution. Calculate four value streams, stress-test them by halving lift assumptions, and replace every year-one estimate with your own 90-day baseline before you request year-two budget.
SOC 2 Type II and Staff WiFi: Passing the Key Controls on Your Wireless Network
You will be able to map each of the key SOC 2 Type II controls to your staff WiFi and close the gaps auditors find. You can then choose between 802.1X, iPSK and a segregated WPA2-PSK network for each device class. Finally, you will know how to prepare access points, controllers and BYOD for a SOC 2 Type II audit.
People counting: WiFi vs camera vs door sensor
Decide which people counting technology fits each question you need answered: door sensors for precise entrance totals, overhead cameras for live counts in one zone, and WiFi for venue-wide dwell time and repeat visits. You can then compare accuracy, cost lines and privacy work, pilot against a manual count, and choose a single method or a combination for your property portfolio.
Why hotel-style guest WiFi fails in residential buildings
You will be able to diagnose why residents in Multi-Family properties, Student Housing, and MDUs keep reporting WiFi faults, and choose the authentication model that fixes them. The answer is a per-household iPSK key on your existing access points, with a separate captive portal network kept for visitors.
Presence analytics vs engagement analytics
Decide whether your estate needs presence analytics, engagement analytics or both, based on the question you must answer this quarter. You will know what each layer measures, how MAC randomization limits presence data, which CCPA/CPRA lawful basis applies to each, and how to sequence deployment across multiple sites on the access points you already own.
HPE Aruba Central presence analytics: setup, exports and limits
You will be able to enable Aruba Central presence analytics per site, calibrate the RSSI threshold and dwell boundaries against a ground-truth count, and export site-level aggregates through the Central REST API. You will also know where native presence analytics stops and when a hardware-agnostic platform layer such as Purple earns its place on your existing Aruba access points.
Tenant Session Tracking and Abuse Attribution in Multi-Family WiFi: Mapping Meraki Flows to Purple iPSK Identity
You will be able to trace a single-public-IP abuse notice on a Multi-Family, MDU, or Student Housing network to one apartment. You join Meraki MX flow exports to Purple iPSK identity and RADIUS Accounting records on MAC, VLAN, and time. You will also know the retention, NTP, and drill controls that keep that chain defensible for counsel.
CIPA compliance: compliance checklist for venue operators
You will be able to decide whether CIPA binds your WiFi, then segment networks, route DNS through Purple Shield and close bypass routes. You will also know what evidence to keep for Form 486 or Form 479 certification. The checklist assigns every requirement an owner, so your next funding year certification has nothing missing.
The compliance case for passwordless WiFi: HIPAA, PCI, ISO 27001
You will be able to decide whether moving staff networks from a shared password to 802.1X with EAP-TLS closes your audit gaps under PCI DSS 4.0, HIPAA and ISO 27001:2022. You will know which controls it satisfies, which it does not, and what evidence to assemble before fieldwork.
IronWiFi Alternatives for Enterprise Deployments
You will be able to shortlist an IronWiFi alternative on the jobs your network must do: authentication, identity, consent, hardware coverage and three-year cost. You will know when Purple, Cloud4Wi, Spotipo or Cloudi-Fi fits better, when IronWiFi still wins, and how to run a one-venue pilot that proves each vendor's claims.
iOS and macOS 802.1X troubleshooting: a deployment checklist for Intune, Jamf and Entra ID
Use this checklist to diagnose why iPhones, iPads and Macs fail 802.1X on Intune or Jamf Pro. Each failure maps to one of four causes: server trust, identity certificate, macOS mode or Entra ID group scoping. You will confirm the cause from eapolclient and RADIUS logs, apply the fix and stage future certificate rotations.
Intune WiFi profile server trust: certificate server names and root CA checklist for Entra ID
You will be able to configure the server validation half of an Intune WiFi profile so EAP-TLS and PEAP connect on Windows, Apple and Android. You will match certificate server names to the RADIUS certificate, deploy the correct root CA, align Entra ID group assignments, and stage certificate renewals before they silently break connections.
Android 802.1X and EAP-TLS troubleshooting: a deployment checklist for Intune and Entra ID
You will be able to pinpoint why managed Android cell phones fail EAP-TLS on your staff SSID and fix it in Intune. Match each symptom to the four usual causes - missing CA or domain, client certificate in the wrong profile, a mismatched RADIUS server names value, or an undelivered trusted root. Then apply a rollout checklist that stops repeat outages.
Got questions about your specific setup?
Our team works with venue operators, IT managers, and network engineers across 80,000 venues. Book a 20-minute call and we will show you how others like you solved it.